Information Warfare Strategies (SRF-IWS): Tax Haven Attacks

Desde esta nueva sección del blog, Information Warfare Strategies (SRF-IWS), presentaremos escenarios hipotéticos con relación a un tema muy de moda como es la ciberguerra. Analizaremos el porqué, el cómo y el impacto de realizar ataques a los sistemas informáticos conocidos como Computer Network Attacks (CNA) [1] en la jerga de ciberguerra.

This new section of the blog, Information Warfare Strategies (SRF-IWS), will introduce hypothetical cyber warfare scenarios, a hot topic these days. We will analyze the why, the how and the impact of computer attacks known as Computer Network Attacks (CNA) [1] in cyber warfare jargon.

¿Por Qué? / The Why?

Ataques a los sistemas financieros, en particular a la bolsa, han sido planteados por diversas películas como “Die Hard 4.0” o “Asalto al tren Pelham 123”, además de numerosos ejemplos reales como Rusia acusada por la SEC de manipulaciones en la bolsa mediante el uso de cuentas robadas [2] o los recientes ataques al NASDAQ [3] y al comercio del carbón en Europa [4] con el fin de causar daños económicos, llamar la atención o simplemente enriquecerse.

Attacks to financial systems, in particular the stock market, have been raised by various films such as “Die Hard 4.0″ or ” The Taking of Pelham 123″, as well as numerous real examples as Russia accused by the SEC of manipulation in the stock market through the use of stolen accounts [2] or the recent attacks on NASDAQ [3] and the carbon market in Europe [4] in order to cause economic damage, draw attention to or just to enrich themselves.

En nuestro primer escenario vamos a enfocar nuestro ataque a los paraísos fiscales. Más de un lector se estará preguntando el porqué de esto, pues por varias razones:

  •  Los paraísos fiscales “protegen” una cantidad inimaginable de fortunas de millonarios, empresas, países, dictadores, etc.
  •  La discreción es la norma, ya que tanto a los paraísos fiscales como a sus propios clientes no les interesa que se haga público si los sistemas informáticos han sido comprometidos y las fortunas robadas, aunque dependiendo de quién sea la fortuna podría haber serias repercusiones. 
  •  Si las grandes empresas como Google, Adobe y Yahoo con amplios recursos y talento no fueron capaces de resistir ataques informáticos (Operación Aurora [5]) o el mismísimo Departamento de Defensa americano frecuentemente víctima de ataques, ¿podemos realmente creer que estos paraísos fiscales son seguros y podrían defenderse contra ataques focalizados? Permitidme que lo dude.

In the first scenario we will focus our attacks on Tax Havens. I’m sure more than one reader will be wondering why, well there are several reasons:

  • Tax havens “protect” an unimaginable amount of fortunes from millionaires, companies, countries, dictators, etc.
  • Discretion is the rule, both tax havens and their customers care to go public if computer systems have been compromised and fortunes stolen, although depending on whom the fortune is could have serious repercussions.
  • If large corporations such as Google, Adobe and Yahoo with vast resources and talent were not able to resist attacks (operation Aurora [5]) or even the US Department of Defense often victim of attacks, can we really believe that these tax havens are safe and could defend against targeted attacks? Let me doubt it.

Las Fig. 1 y Fig. 2 son mapas que reflejan los países considerados como paraísos fiscales, aunque algunos países han sido eliminados de esta lista negra recientemente como es el caso de Andorra debido a una mayor transparencia. Estaríamos hablando de alrededor de unos 50 países que podrían ser objetivos potenciales, y podemos apreciar que la mayoría de ellos no destaca por ser tecnológicamente avanzados.

Fig. 1 and Fig. 2 are maps that reflect the countries considered tax havens, although some countries have been removed from this list recently as in the case of Andorra because of greater transparency. We would be talking about some 50 countries that could be potential targets and we can see that most of them are not noted for being technologically advanced.
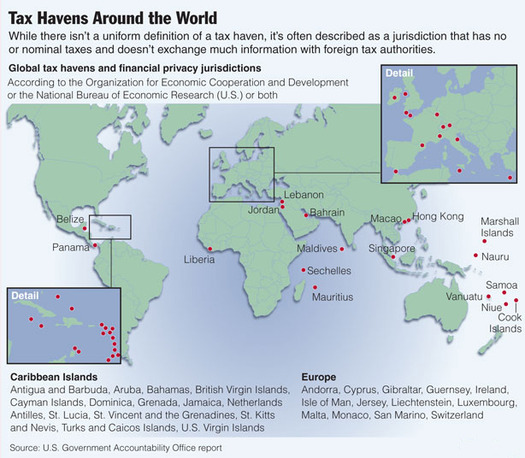
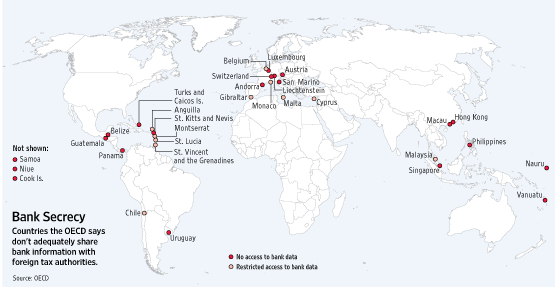
Fig. 1 – Paraíso Fiscal Mapa I / Tax Haven World Map I

Fig. 2 – Paraíso Fiscal Mapa II / Tax Haven World Map II

 Computer Network Operations (CNO) / Cyber Operations (CO) / Computer Network Operations (CNO) / Cyber Operations (CO)

Computer Network Operations (CNO) es el término que engloba las acciones relacionadas con la ciberguerra y que contiene 3 categorías:

  • Computer Network Attack (CNA): Ataque
  • Computer Network Defense (CND): Defensa
  • Computer Network Explotation (CNE): Inteligencia

En esta sección hablaremos sobre ataques teóricos a nuestros objetivos por lo que estaremos interesados en CNA y CNE. 

Computer Network Operations (CNO) is the term that includes actions relating to cyber warfare and contains 3 categories:

  • Computer Network Attack (CNA): Attack
  • Computer Network Defense (CND): Defense
  • Computer Network exploitation (CNE): Intelligence

In this section we will discuss theoretical attacks for our goals, therefore we are interested in CNA and CNE only.

En la pasada edición de Defcon, el legendario congreso hacker, hubo una interesante charla sobre la creación de un ficticio ciber-ejército capaz de atacar cualquier país por Charlie Miller, reputado experto en seguridad. Miller en su exposición planteaba la idea que Corea del Norte le secuestraba y le obligaba a crear un ciber-ejército capaz de comprometer la seguridad de los EE.UU. Para ello Miller estimo que necesitaría unas 592 personas  (expertos en seguridad, programadores, jefes de proyecto, etc.) con un prepuesto de 49 millones de dólares y un plazo de 2 años para conseguir este objetivo. [6]

In the last Defcon, the legendary hacker Congress, there was an interesting talk on the creation of a fictional Cyber-army capable of attacking any country by renowned security expert Charlie Miller. Miller in his presentation raised on the idea that North Korea kidnapped him and obliged him to create a cyber-army capable of compromising the security of the United States. So Miller estimated that it would require about 592 people (security experts, developers, project managers, etc.) with a budget of $49 million and a timeframe of 2 years to achieve this goal. [6]

Nuestro comando es más modesto y basado en la metodología de Miller estimamos que necesitamos unas 27 personas (seguridad, pentester y jefes de proyecto) y un presupuesto de unos 3 millones de dólares pero esto no incluye equipamiento, gente externa, nuestro equipo de agentes en el terreno para ataques físicos o la gente de desarrollo. Botnets que en este caso no emplearemos (en caso de necesitar botnets podemos alquilar en el mercado negro). Como resultado final estaríamos hablando de unas 40 personas con un presupuesto de 5 millones de dólares en un periodo de 6-9 meses, siempre que queramos hacerlo de forma profesional. Posiblemente podamos conseguirlo con menos gente y presupuesto.

Our commando is more modest and based on Miller’s methodology we believe that would require around 27 people (security experts, pen tester and project managers) and a budget of about $3 million, but this amount does not include equipment, external people, our team of field agents to perform physical attacks or developers. Botnet that in this exercise will not be used (in case of needing botnets we can rent them on the black market). The end result would be around 40 people with a budget of $5 million over a period of 6-9 months, wherever we want to do it professionally. We can possibly get it with fewer people and budget.

La combinación de ataques es un concepto que debemos dominar para conseguir nuestro objetivo como nos enseña “Unrestricted Warfare”, por lo que usaremos distintas estrategias de ataque como:

  • Informáticos: mediante nuestro equipo de ciber soldados
  • Política: si tenemos la capacidad como Nación de ejercer algún tipo de fuerza política/económica contra alguno de estos paraísos. Algún tipo de embargo referente a tecnologías de seguridad podría ser interesante para nuestra ventaja
  • Terroristas: mediante nuestros agentes de campo

Nuestro planteamiento de ataque es que para ser más efectivos y conseguir nuestro objetivo debemos tener un equipo de agentes en el terreno y no sólo ciber soldados a distancia, aunque quién sabe, quizá es lo único que necesitamos.

The combination of attacks is a concept that we must master to achieve our goals, as the “Unrestricted Warfare” teach us, and by which we will use different attack strategies such as:

  • Computer: through our team of cyber warriors
  • Politics: if we have the ability as a State-Nation to exercise some sort of policy/economic force against any of these tax havens. Any type of embargo concerning security technologies might be interesting to our advantage
  • Terrorists: through our field agents

Our attack approach is that in order to be more effective and achieve our goals we must have a team of field agents and not only cyber warriors from a remote location, but who knows, maybe it is all that we need at the end.

En base a nuestra combinación de ataques hemos desarrollado un mapa de ataque simple (Fig. 3) que nos da una visión de posibles estrategias que podemos seguir para alcanzar nuestro objetivo.

On the basis of our attack combination we have developed a simple attack map (Fig. 3) that gives us a vision of possible strategies that we can execute to achieve our goals.
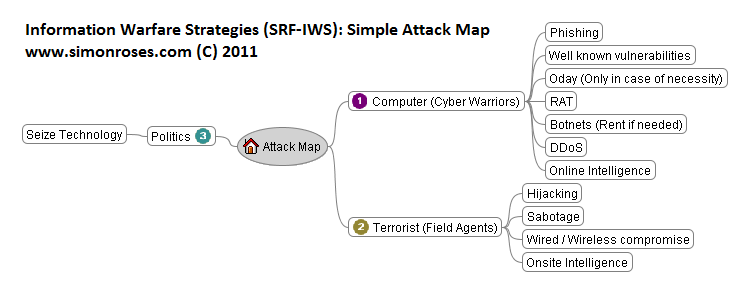
Fig. 3 – Mapa de ataque simple / Simple Attack Map

Ahora ya estamos listos para la acción!

Now we are ready for action!

Impacto Económico / Economic Impact

Se desconoce el volumen económico que manejan los paraísos fiscales, pero el senado de EE.UU. estima que solamente EE.UU. pierde unos 100 billones de dólares anuales por evasión de impuestos a través de estos paraísos fiscales y si incluimos otros países estaríamos hablando de billones de euros. [7]

The economic volume operating in tax havens is unknown, but the United States Senate considers that United States alone losses some $100 billion a year for tax evasion through these tax havens and if we include other countries we would be talking of billions euros in losses. [7]

Si quisiéramos provocar daños económicos a un país podríamos intentar averiguar cuáles son los paraísos fiscales preferentes y atacarlos. Por ejemplo en España hace unos años Andorra y Gibraltar eran bastante populares entre empresas, pequeños inversores y deportistas.

If we were to cause economic damage to a country we could try to find out what are the preferential tax havens and attack them. For example in Spain a few years ago Andorra and Gibraltar were quite popular among companies, small investors and athletes.

Un ejemplo real del uso de estas tácticas ocurrió en 1999 cuando operativos de la CIA y posiblemente de la NSA bajo un mandato del Presidente Bill Clinton obtuvieron permiso para comprometer la seguridad de varios bancos en Rusia, Chipre y Grecia con el fin de embargar las cuentas bancarias de Slobodan Milosevic acusado de crímenes de guerra. La operación fue todo un éxito y demostró el beneficio de estas tácticas. [8]

 A real example of the use of such tactics occurred in 1999 when operatives of the CIA, and possibly of the NSA under a mandate from President Bill Clinton got permission to compromise the security of several banks in Russia, Cyprus and Greece in order to seize bank accounts of Slobodan Milosevic, accused of war crimes. The operation was a success and showed the benefit of these tactics. [8]

El paraíso fiscal por excelencia es Suiza, aunque en los últimos años han sufrido diversos ataques informáticos, robo de información y en un esfuerzo en ganar transparencia han provocado que haya dejado de ser un paraíso fiscal para muchos millonarios pero a pesar de ello sigue siendo un objetivo atractivo para nuestro escenario.

The tax haven per excellence is Switzerland but in recent years they have suffered various computer attacks, information leakage and in an effort to gain transparency have resulted in that it has ceased to be a tax haven for many millionaires but nevertheless continues to be an attractive target for our scenario.

Dicho esto debido a la poca información que existe sobre el volumen de negocio que manejan los paraísos fiscales es difícil estimar el impacto económico, pero el lector puede estar seguro que comprometer algunos de estos paraísos fiscales puede tener severas consecuencias económicas para muchas empresas a nivel global.

Having said that, due to the little information that exists on the volume of business that tax haven manages is difficult to estimate the economic impact but the reader can be sure that owning some of these tax havens can have severe economic consequences for many companies at a global level.

Conclusiones / Conclusions

A lo largo de este ficticio escenario hemos analizado el porqué, el cómo y el impacto de realizar ataques a objetivos concretos mediante ciberguerra. Como ya hemos señalado los paraísos fiscales pueden ser un objetivo lucrativo y tener unas consecuencias serias a nivel global sobre todo en el periodo de crisis que nos encontramos.

In this fictional scenario we’ve analyzed the why, the how and the impact of strikes at specific targets by cyber warfare tactics. As we have already mentioned tax havens can be a lucrative target and have serious consequences at the global level particularly in the period of crisis that we are living.

Podemos resumir este escenario en:

  • Difícilmente cualquier país, empresa o Infraestructura Crítica (IC) podrá defenderse de ataques bien organizados.
  • Hemos creado un pequeño ciber ejército pero es factible a menor escala, como operan los grupos mafiosos en la Red.
  • Debemos definir nuestro plan de acción y tener los recursos necesarios.
  • La ciber guerra existe y los países tienen que ser conscientes y adoptar medidas.
  • Es necesaria una coordinación entre lo civil y militar para defender los intereses nacionales.

We can summarize the scenario:

  • Hardly any country, corporation or Critical Infrastructure (CI) can defend against organized attacks.
  • We have created a small Cyber Army but it is feasible on a smaller scale, as operate mafia-style groups on Internet.
  • We must define our action plan and have the necessary resources.
  • Cyber warfare exists and countries need to be aware and take action.
  • Coordination between civil and military to defend national interests is a must.

Sin duda veremos el uso de estas tácticas de forma frecuente y profesionalizada y muchos de los perfiles necesarios serán profesiones en auge en esta década.

Desde aquí invitamos al lector a que nos haga sugerencias de escenarios que le gustaría que desarrollemos en conjunto.

Hasta el próximo SRF-IWS!!!!!

We will certainly see the use of these tactics more frequently and professionally and many of the necessary skills will be jobs on the rise in this decade.

From here we invite the reader to make us suggestions of scenarios that you would like us to develop together.

Until the next SRF-IWS!

— Simon Roses Femerling

Enlaces / Links

[1] http://en.wikipedia.org/wiki/Computer_network_operations

[2] http://www.v3.co.uk/v3-uk/news/1960891/russian-accused-stock-hacking-denies-allegations

[3] http://online.wsj.com/article/SB10001424052748704709304576124502351634690.html

[4] http://www.ens-newswire.com/ens/jan2011/2011-01-20-01.html

[5] http://en.wikipedia.org/wiki/Operation_Aurora

[6] http://www.defcon.org/images/defcon-18/dc-18-presentations/Miller/DEFCON-18-Miller-Cyberwar.pdf

[7] http://www.oecd.org/document/21/0,3746,en_2649_37427_42344853_1_1_1_37427,00.html

[8] http://www.zdnet.com/news/cias-cyberwar-is-just-computer-crime/102411

http://newunionism.wordpress.com/2010/11/24/tax-havens-and-globalisation/
http://www.namebase.org/news11.html

Posted in Economics, Hacking, Security, Technology | Tagged , , , , , , , , , | Leave a comment

Book Review: 30 Arduino Projects for the Evil Genius

Sin duda Arduino está de moda y este libro escrito por Simon Monk nos introduce en el mundo de Arduino y la electrónica de forma muy práctica y sencilla mediante 30 ejemplos. 30 Arduino Projects for the Evil Genius (ISBN-13: 978-0071741330) de la serie Evil Genius está dividido en 10 capítulos que tratan diferentes aspectos del uso de arduino como el uso de LEDS, sensores, luces, sonido, etc.

No doubt Arduino is a hot topic and this book written by Simon Monk introduces us to the Arduino world and electronics in a very practical and simple way through 30 examples. 30 Arduino Projects for the Evil Genius (ISBN-13: 978 – 0071741330) of the Evil Genius series is divided into 10 chapters dealing with different aspects of the use of arduino such as the use of LEDS, sensors, lights, sound, etc.

Para los amantes de la electrónica o aquellos que se quieran introducir es desde luego una obra de recomendada lectura  por su sencillez y los extensos conocimientos del autor sobre la materia. Sin embargo se echa en falta algo más del uso de Arduino en redes wifi, bluetooth o comunicación con otros dispositivos.

For Electronics lovers or those who want to learn about it this is certainly a recommended reading due to its simplicity and the extensive knowledge of the author on the subject. However the book lacks about Arduino use in wifi networks, Bluetooth or communication with other devices.

Algunos proyectos son realmente fascinantes como jugar con un rayo láser, la creación de una puerta magnética o la gestión de la temperatura en el hogar :)

Some projects are really fascinating like how to play with lightning laser, a magnetic door creation or temperature management at home :)

A pesar de sus carencias es un libro de lectura rápida y fácil para todas las edades ya que parte que el lector no tiene conocimientos en la materia pero también puede ser leído por usuarios avanzados para comparar formas de pensar.

In spite of its shortcomings it is a quick and easy reading for all ages as the book parts the reader has no knowledge on the subject but it can also be read by advanced users to compare ways of thinking.

No debemos olvidar que esta saga de libros, Evil Genius, cuenta con otras obras igualmente atractivas.

We must not forget that this series of books, Evil Genius, has other equally attractive topics.

Puntación (1 rosa, muy malo / 5 rosas, muy bueno): 4 Rosas (Lectura Recomendada)

Score (1 rose, very bad / 5 roses, very good): 4 Roses (Recommended Reading)

— Simon Roses Femerling

Posted in Books, Technology | Tagged , , , | 1 Comment

Metasploit PRO In Action

En este post haremos un tour de metasploit PRO, un GUI comercial con importantes mejoras para el conocido metasploit que nos permite convertirnos en experto pentester de forma rápida y sencilla.

In this post we will make a tour of metasploit PRO, a commercial GUI with significant improvements to the known metasploit allowing us to become a pentester expert quickly and easily.

Metasploit PRO nos guiará por todo el ciclo de un pentest mediante un sencillo y elegante interfaz web como descubrimiento, explotación, recogida de información y generación de informes, etc.

Metasploit PRO will guide us on the whole pentest cycle using a simple and elegant web interface as discovery, exploitation, information collection and generation of reports, etc.

Aunque utilicemos metasploit PRO o la versión Express, el hermano pequeño, es recomendable conocer el uso de la línea de comandos en metasploit para convertirnos en maestros de metasploit!

Although we use metasploit PRO or Express, the little brother, is recommended to know the command line use of metasploit to become a master of metasploit!

Para este ejemplo realizaremos un ataque al metasploitable, una máquina virtual Linux vulnerable que Rapid7 pone a disposición para hacer pruebas.

For this example we will make an attack on the metasploitable, a vulnerable Linux virtual machine created by Rapid7 available for testing.

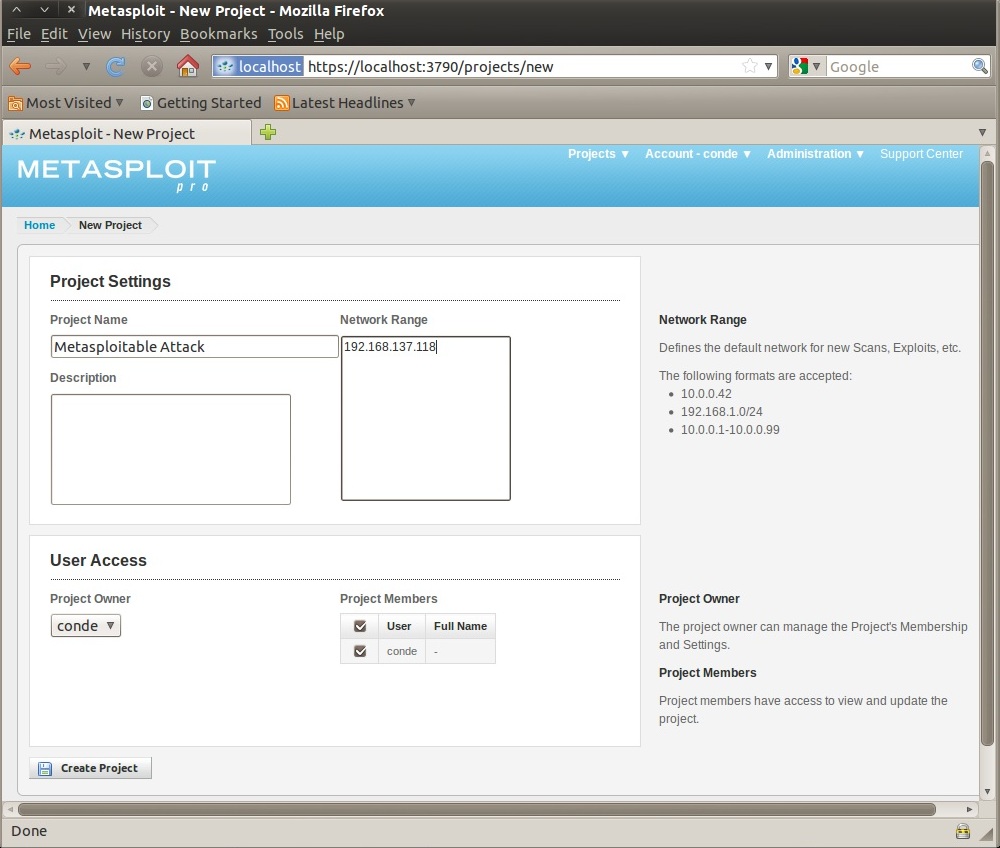
El proceso de instalación y configuración es tan sencillo que no entraremos en detalles. Una vez que tengamos arrancado el metasploit PRO abrimos el navegador, entramos con nuestra cuenta y veremos una pantalla que nos pedirá crear un proyecto. (Fig. 1)

The installation and configuration process is so easy that we will not go into details. Once we have started the metasploit PRO open a browser, enter our account and will see a screen asking us to create a project. (Fig. 1)

Fig. 1 – Creando un proyecto / Create a project

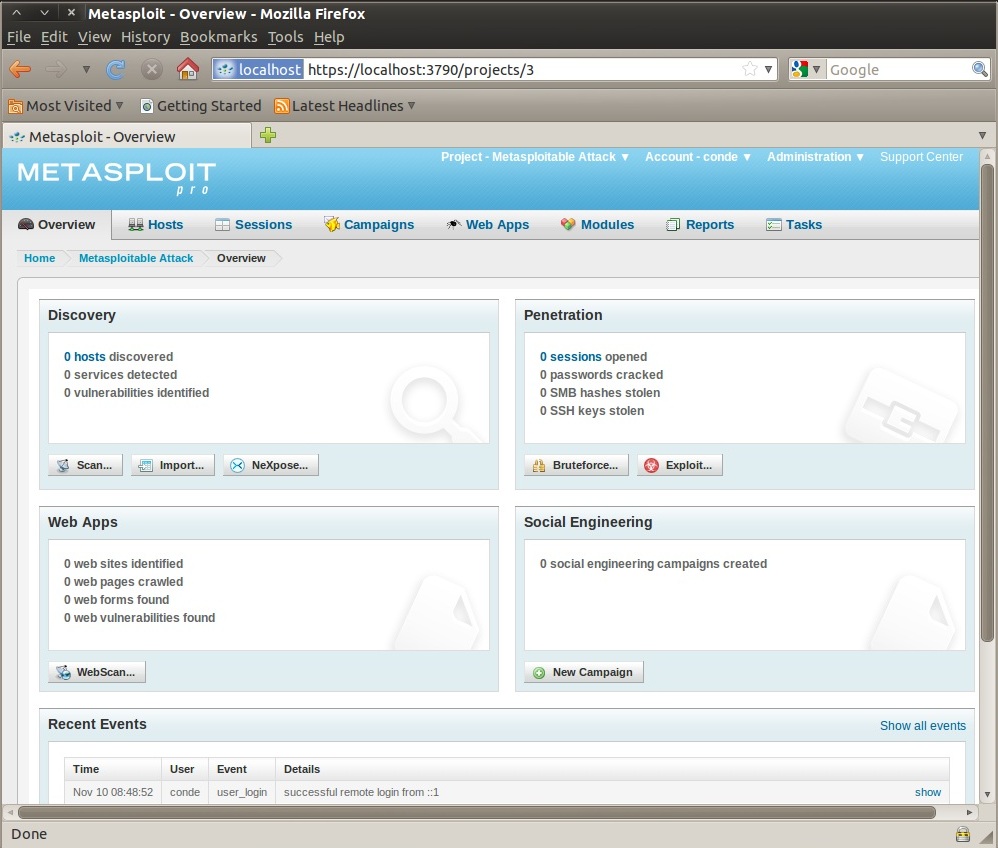
Una vez creado un proyecto, ahora tendremos varias opciones para comenzar nuestro pentest como vemos en la siguiente imagen. (Fig. 2)

Once created a project, we will have several options to begin our pentest as we see in the image below. (Fig. 2)

Fig. 2 – Opciones de pentesting / Pentesting options

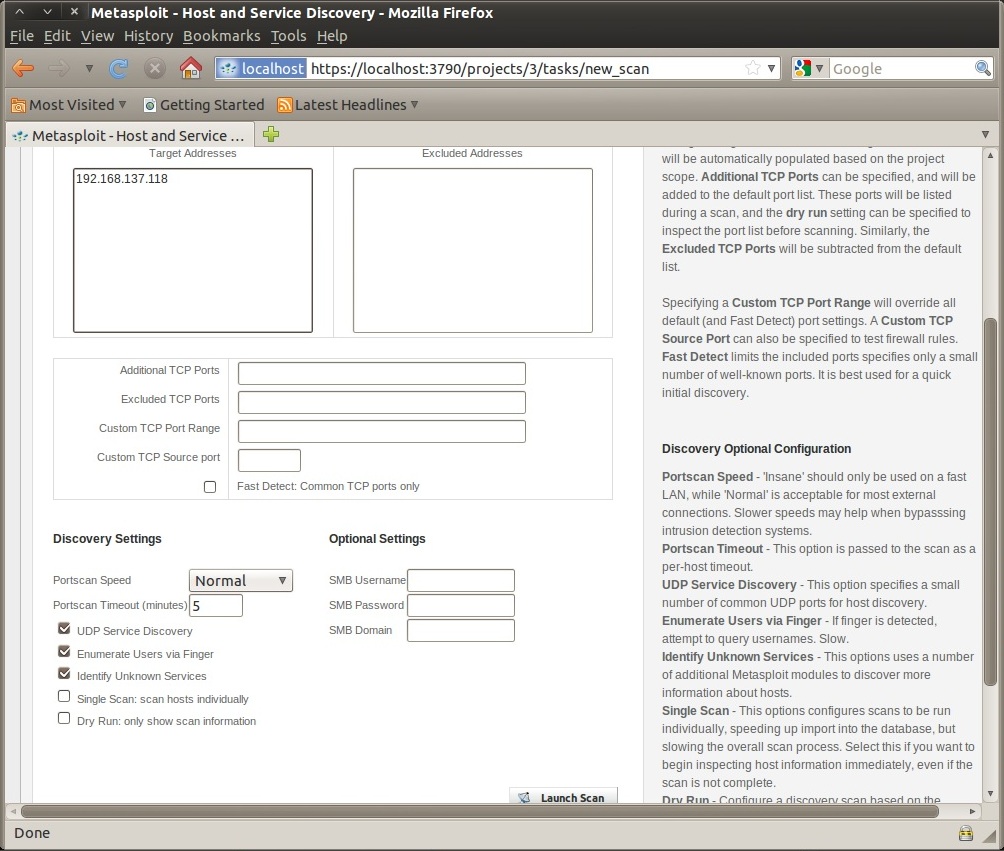
Siguiendo el ciclo de pentest vamos a proceder a realizar un “discovery” para identificar posibles objetivos. Para ello configuramos el rango IP que queramos escanear y demás opciones. (Fig. 3)

Following the pentesting cycle we will proceed to do a “discovery” to identify potential targets. Set the IP range you want to scan and other options as well. (Fig. 3)

Fig. 3 – Escaneo de red / Network scan

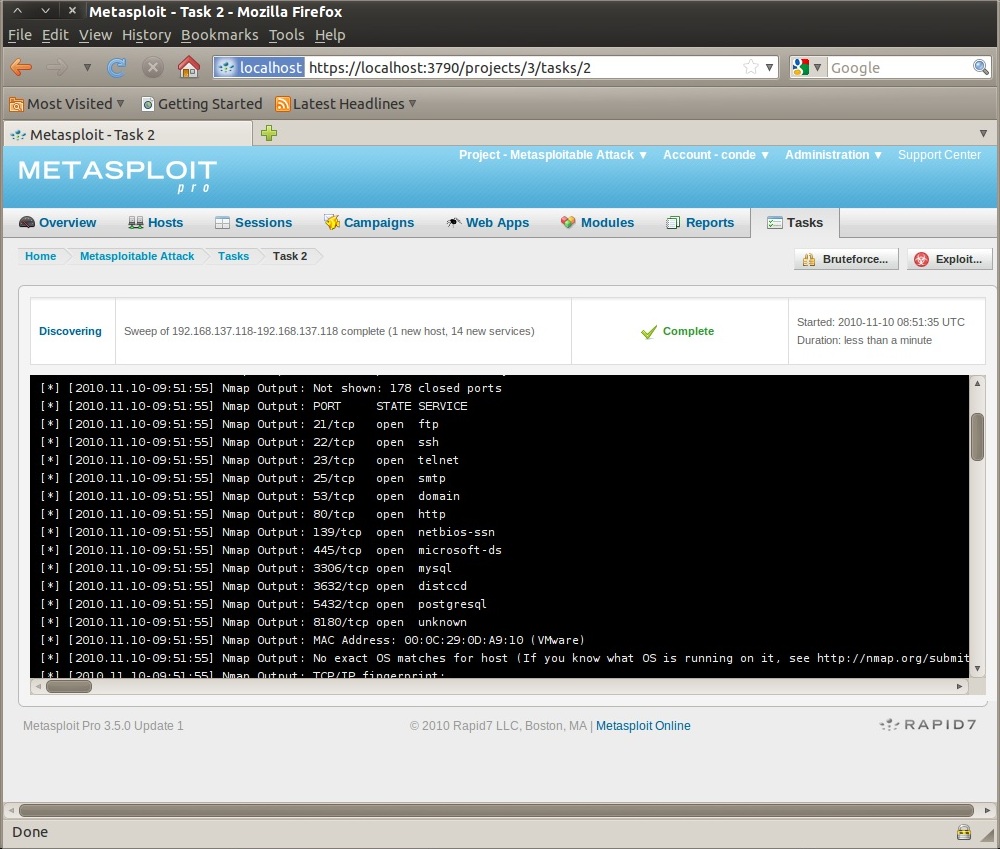
La Fig. 4 nos muestra los resultados del escaneo y encontró una máquina con los siguientes servicios. El escaneo se realiza utilizando Nmap.

The Fig. 4 shows the results of the scan and did found a machine with the following services. Scanning is performed using Nmap.

Fig. 4 – Resultado del Escaneo / Scanning output

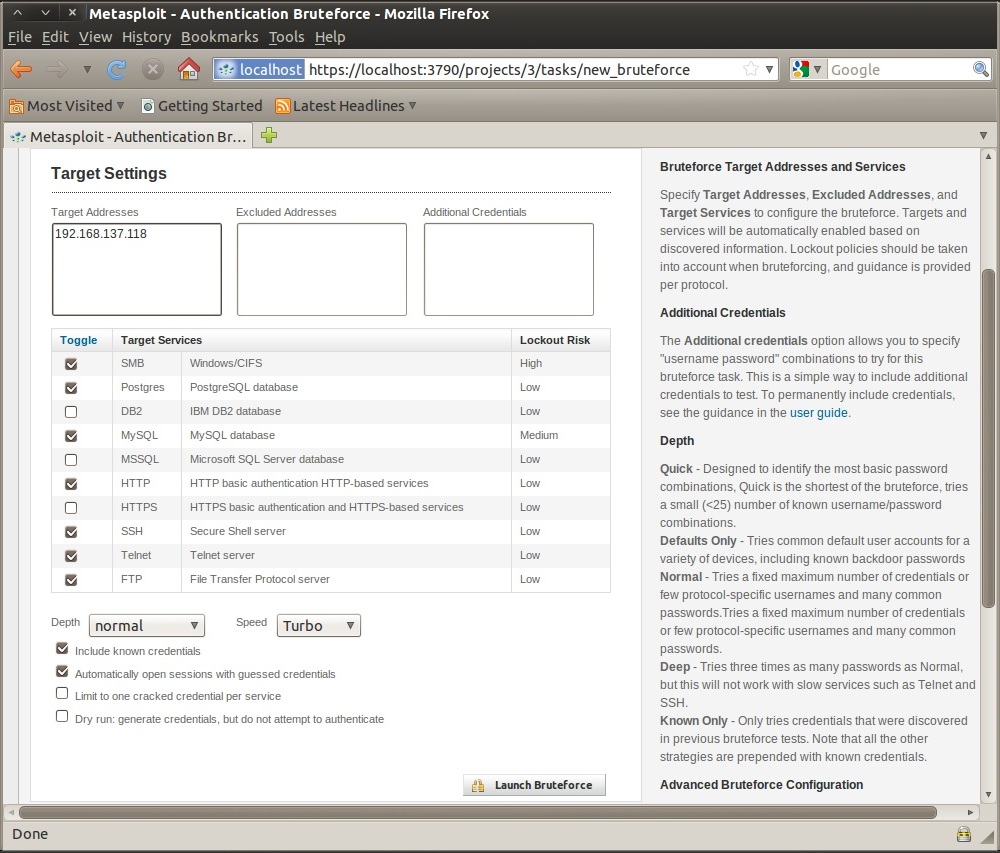
Ahora que ya tenemos un sistema identificado podemos lanzar un ataque de fuerza bruta para probar contraseñas débiles o conocidas. Es importante tener en cuenta que este tipo de ataques suelen durar tiempo (en mi caso duró 2 horas y eso que ambas máquinas están en la misma red) y además son muy ruidosos, posiblemente harán saltar alarmas en cortafuegos e IDS. Si queremos ser silenciosos no hagáis este tipo de ataques. Ver Fig. 5 para ver la configuración de este ataque.

Now that we have identified systems we can launch a brute force attack to prove weak or known passwords. It is important to note that such attacks are often slow and time consuming (in my case it lasted 2 hours and both machines are on the same network) and they are also very noisy, possibly generating alarms in firewall and IDS. If we want to be silent do not do these kinds of attacks. See Fig. 5 to view the configuration of this attack.

Fig. 5 – Configuración fuerza bruta / Brute force configuration

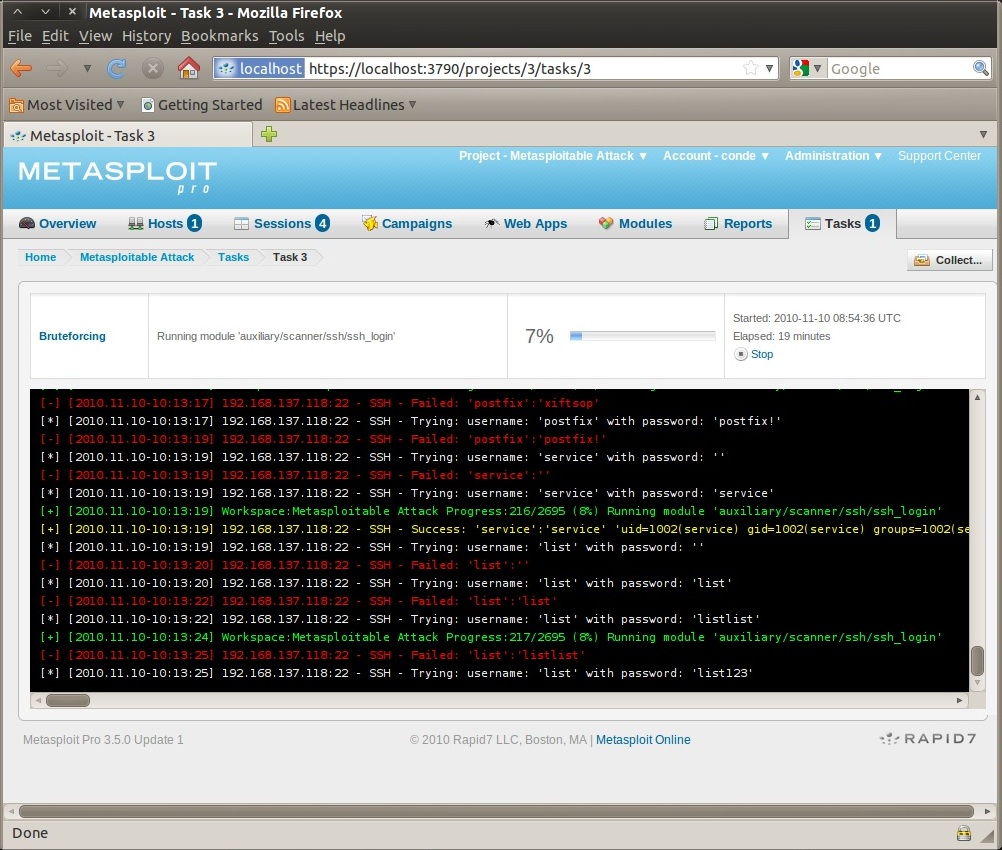
Una vez configuradas las opciones de fuerza bruta comenzamos el ataque y en la Fig. 6 podemos ver como se está ejecutando el ataque y que ha descubierto una contraseña en el servicio SSH. Una ventaja de metasploit PRO es que al realizar este ataque y al adivinar una contraseña nos creará una sesión en la máquina comprometida de forma automática.

Once configured brute force options start the attack and in Fig. 6 we can see the attack in action and that it has discovered a password in the SSH service. One advantage of metasploit PRO to carry out this attack is that when it guesses a password it creates a session in the compromised machine automatically to carry further attacks from inside.

Fig. 6 – Ataque fuerza bruta en acción / Brute force attack in action

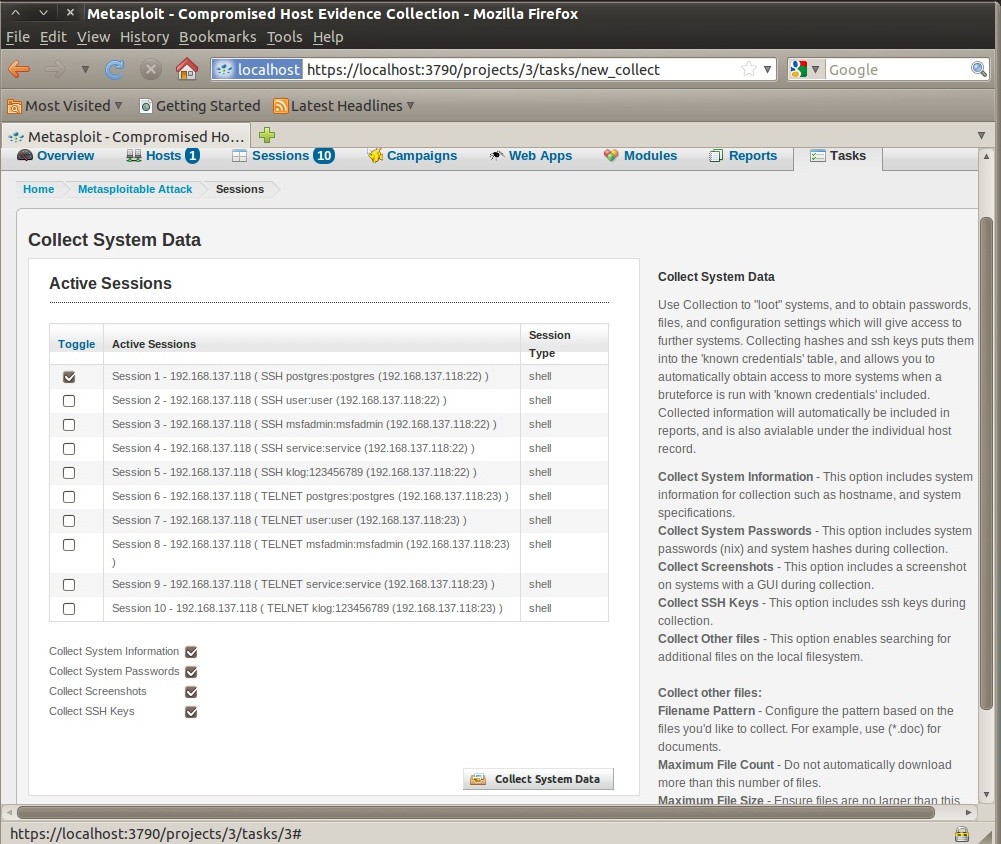
Ahora que ya tenemos una máquina comprometida, en este caso mediante un ataque de fuerza bruta, vamos seguir el orden lógico del ciclo de pentest, por lo que vamos recoger información interna del sistema. (Fig. 7)

Now that we have a compromised system, through a brute force attack, we will follow the logical order of pentesting cycle and collect internal information from the system. (Fig. 7)

Fig. 7 – Recogida de información / Information collection

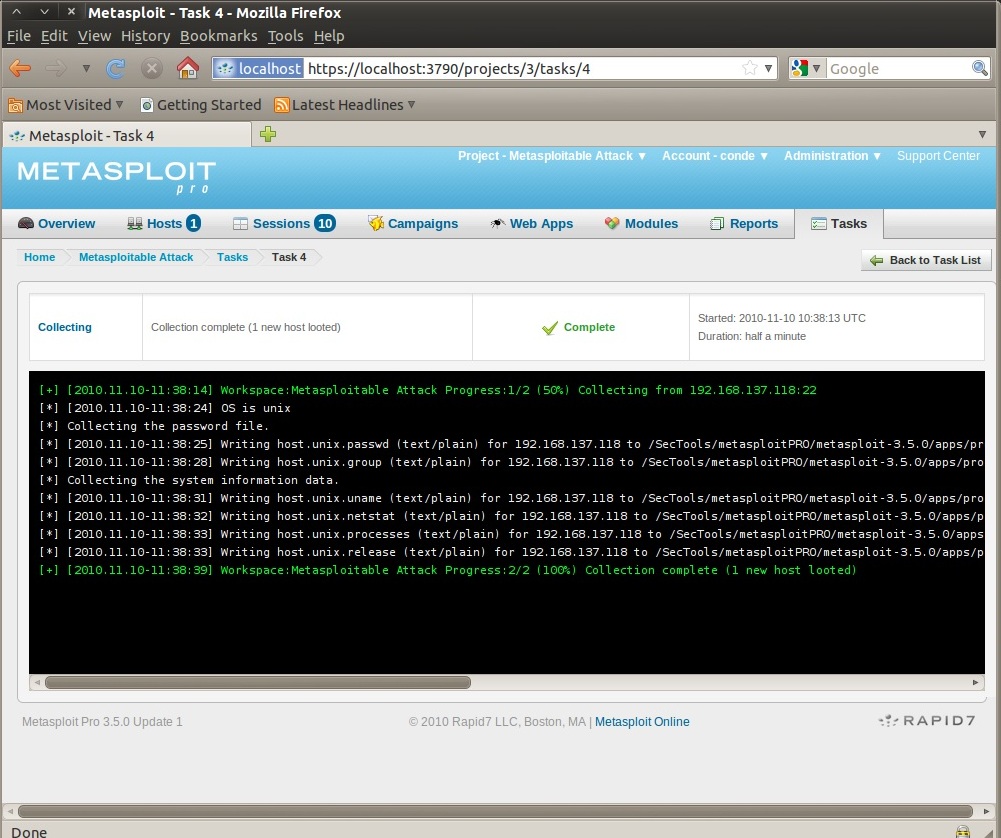
La Fig. 8 nos nuestra el resultado de la recogida de información.

Fig. 8 shows us the result of information collection.

Fig. 8 – Recogida de información en acción / Information collection in action

Es un buen momento para darnos cuenta de que en poco tiempo y de forma organizada hemos identificado sistemas, hemos lanzado ataques de fuerza bruta, hemos comprometido una máquina y obtenido información interna para seguir nuestro pentest. Fascinante y todavía no hemos lanzado ningún exploit ;)

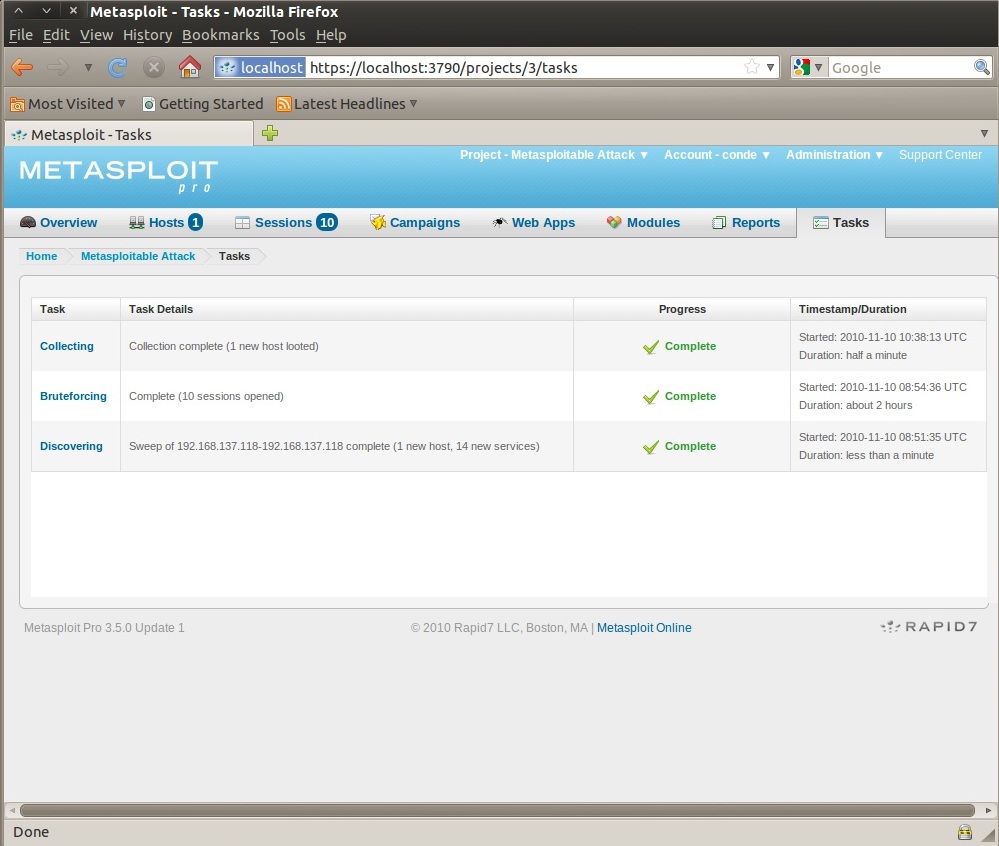
Metasploit PRO guarda todo el historial de las actividades que hemos realizado como podemos apreciar en la Fig. 9 y es muy práctico para saber qué hemos hecho y qué nos falta, sobre todo cuando estamos atacando multitud de máquinas.

It is a good time to realize that in a short time and in an organized manner we have discovered systems, launched brute force attacks, compromised systems and obtained internal information to keep carrying out our pentesting. Fascinating and still we have not launched any exploit ;)

Metasploit PRO keeps record of all activities that we have carry out as we can be seen in the Fig. 9 and it is very handy to know that we have done so far and what is still missing especially when we are attacking several systems.

Fig. 9 – Historial de actividad / Task History

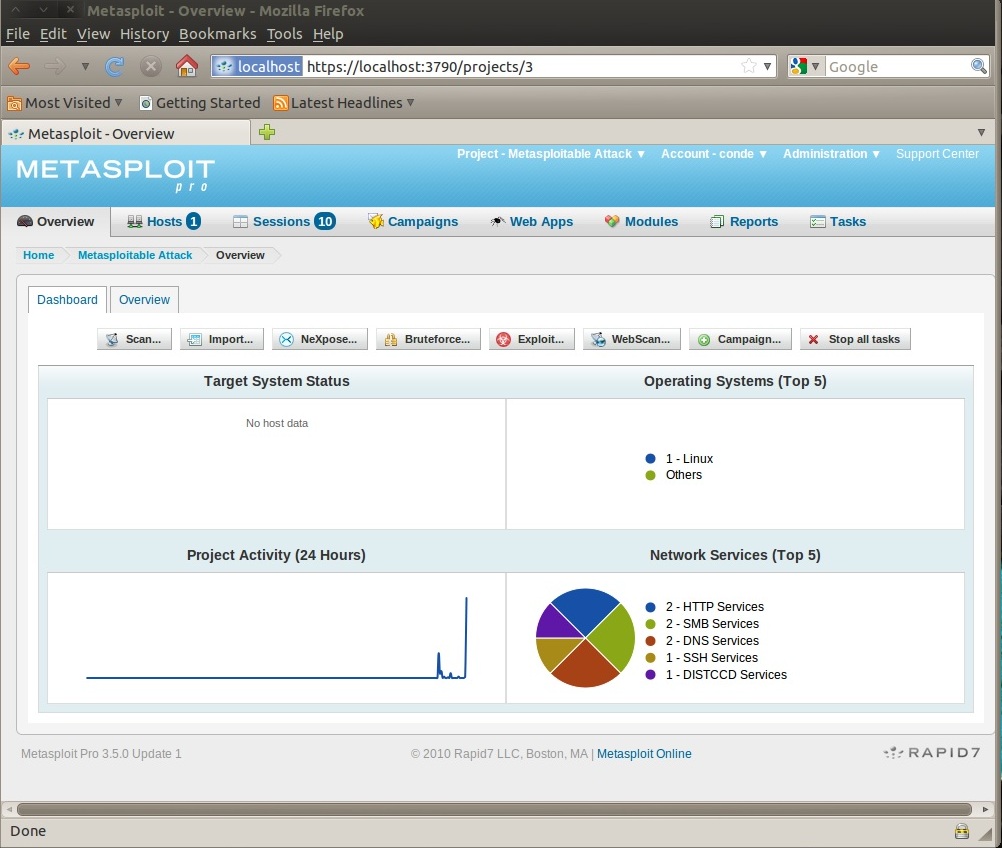
Metasploit PRO nos ofrece un scoreboard que nos muestra el número de máquinas identificadas, comprometidas, servicios, etc. como podemos ver en la Fig. 10.

Metasploit PRO offers us a scoreboard that shows the number of discovered systems, compromised, services, etc. as we see in Fig. 10.

Fig. 10 – Scoreboard / Scoreboard

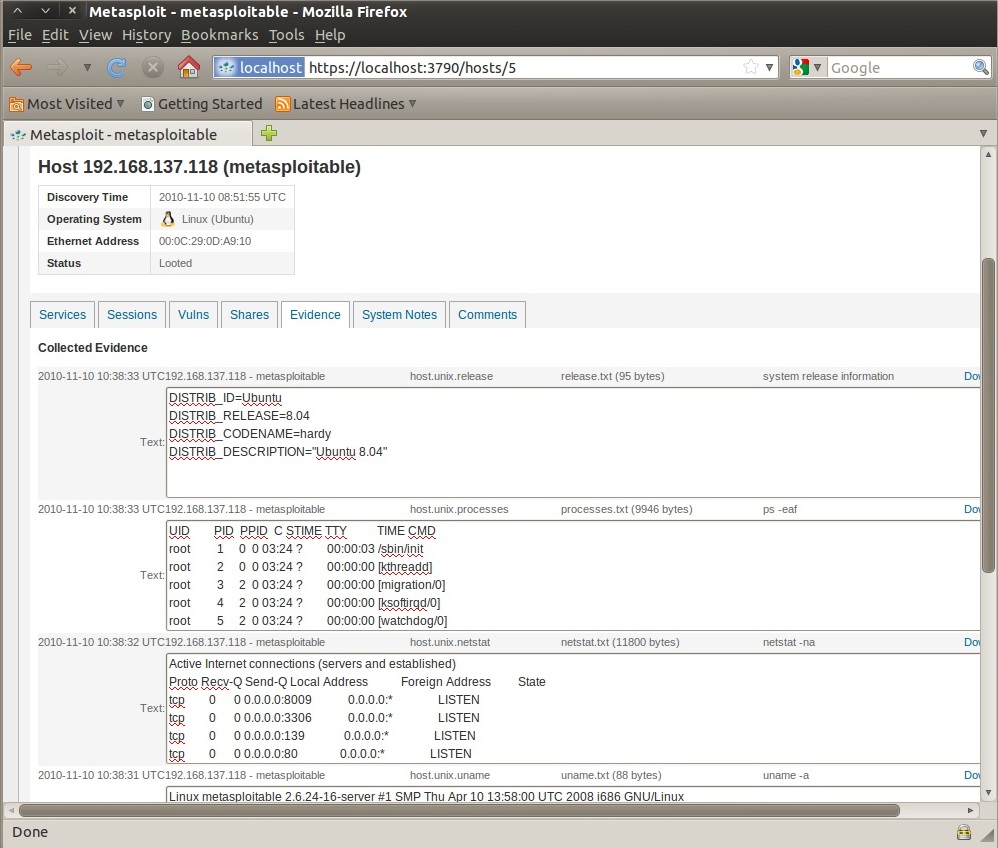
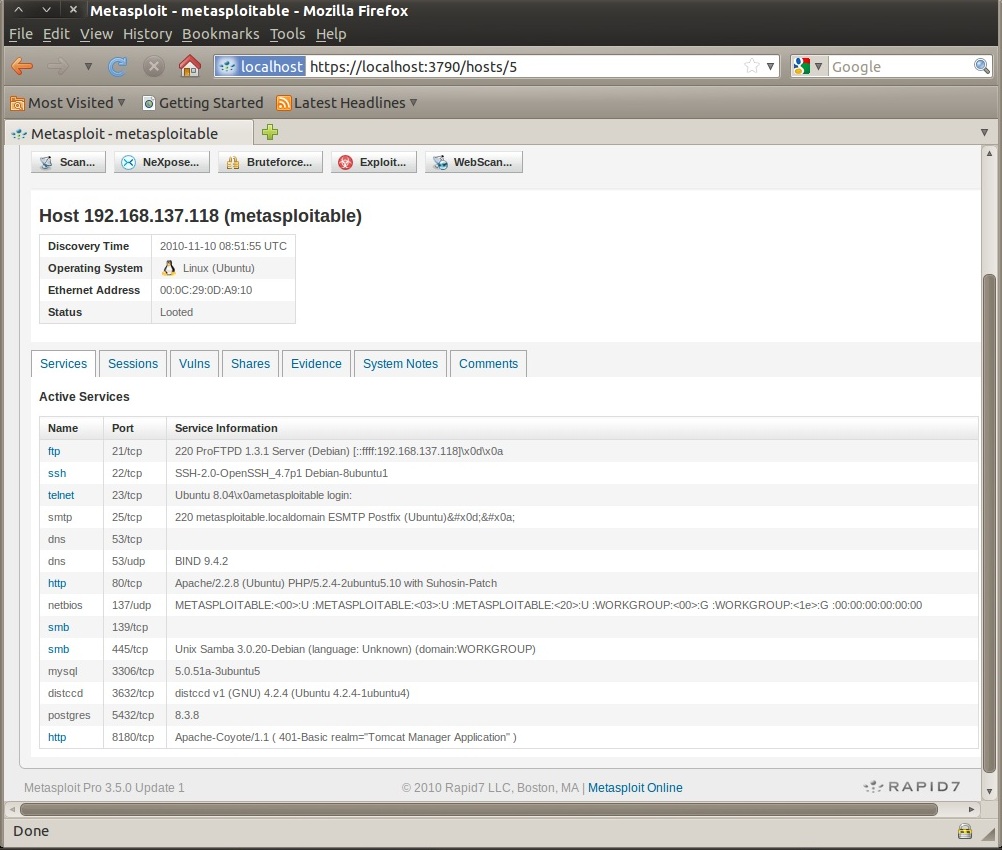
Como es lógico desde el interfaz podemos seleccionar las máquinas que hayamos identificado/atacado para ver toda la información que tengamos sobre ellas.

Las Fig. 11 y Fig. 12 nos revelan los servicios y la información recogida de un sistema que hemos comprometido anteriormente.

Logically from the interface you can select the systems discovered/attacked to see all the information we have about them.

The Fig. 11 and Fig. 12 reveal services and collected information from a system that we have previously compromised.

Fig. 11 – Información del sistema comprometido I / Collected Information I
Fig. 12 – Información del sistema comprometido II / Collected Information II

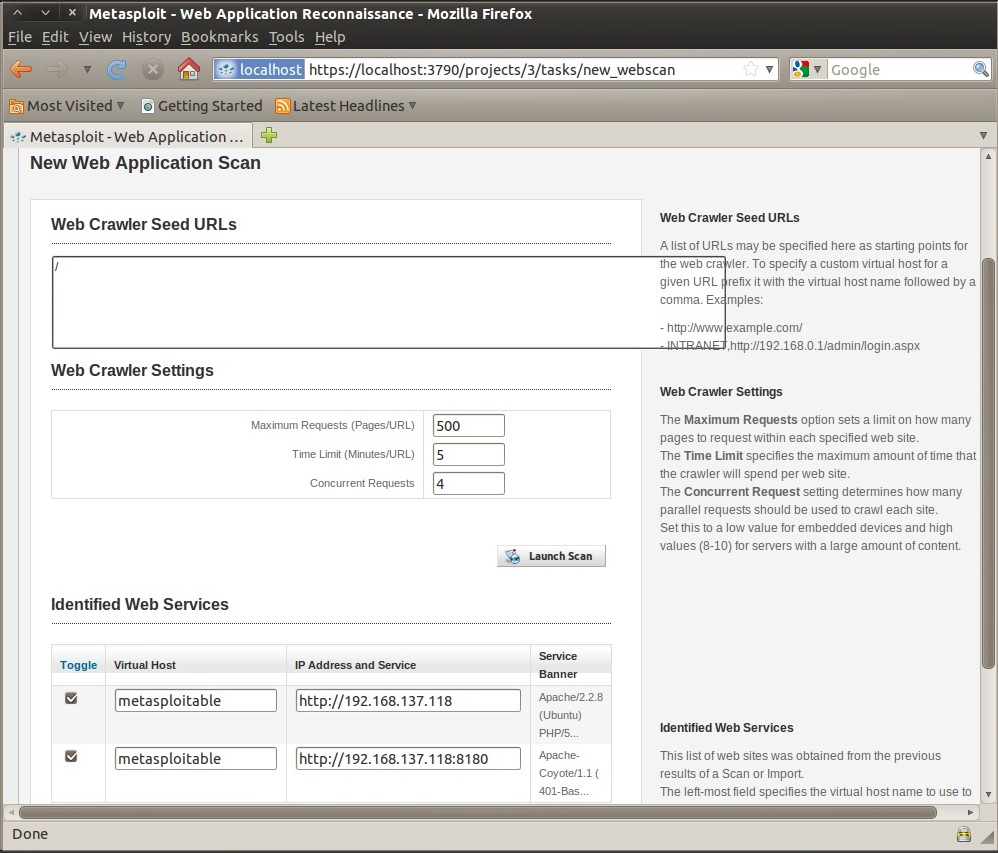
Si observamos los servicios veremos que el sistema atacado tiene web, por lo que sería un buen momento para lanzar un ataque web y descubrir más vulnerabilidades que podamos explotar. J

La Fig. 13 nos nuestra la configuración para realizar un escaneo web, un crawler del sitio web.

If we look at the services we will see that the attacked system has web services so it would be a good time to launch a web attack and discover more vulnerabilities we can exploit J

Fig. 13 shows us the options to perform a website scan, a website crawler.

Fig. 13 – Configuración escaneo web / Web scanning options

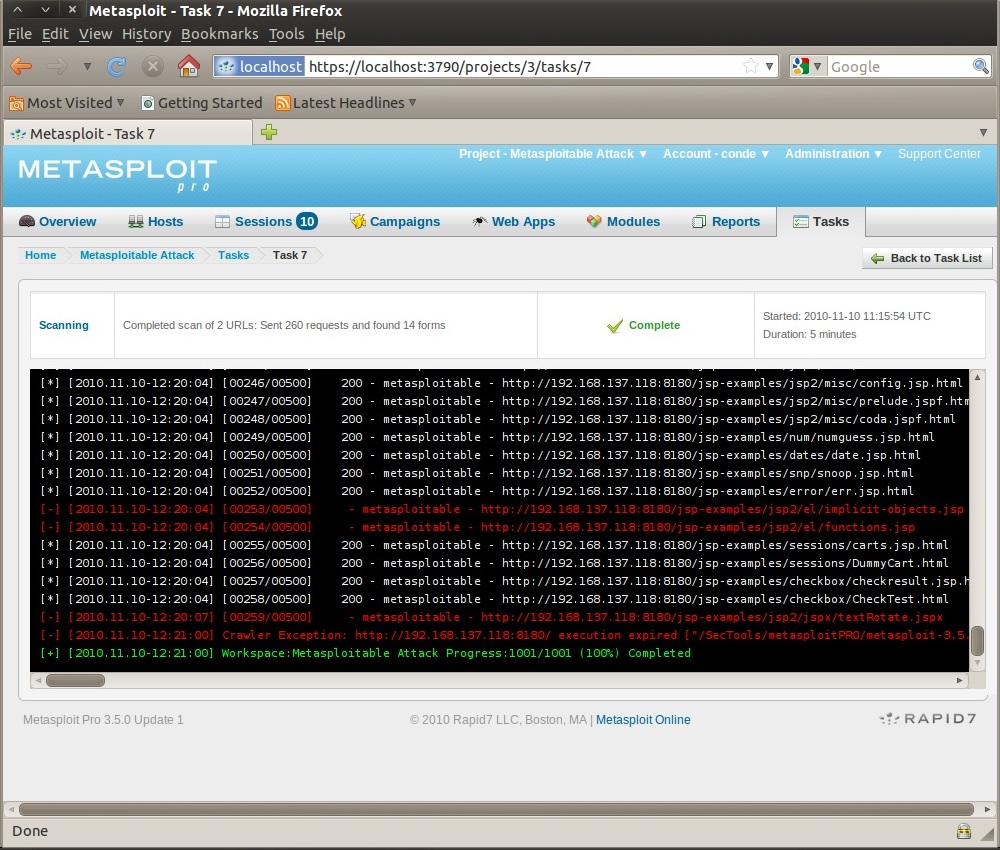
En la Fig. 14 podemos ver el escaneo web en acción.

In the Fig. 14 we can see the web scan in action.

Fig. 14 – Escaneo web en acción / Web scanning in action

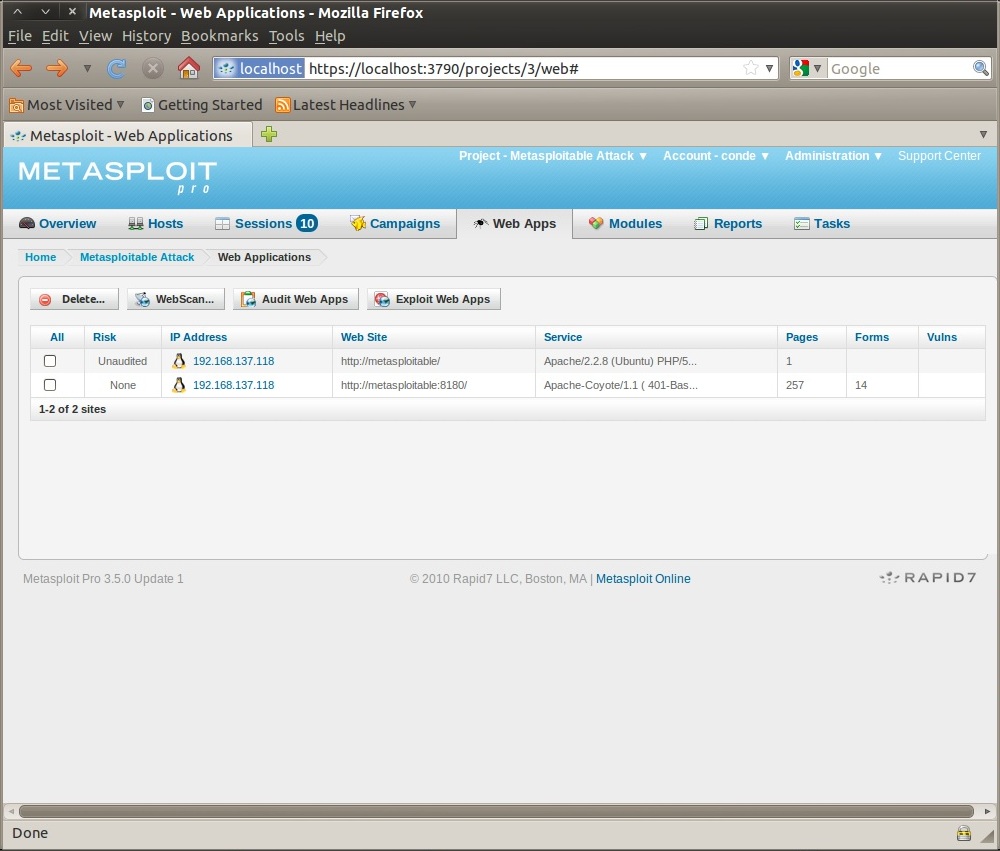
Ahora que ya hemos realizado un escaneo del sitio web (crawling) podríamos realizar acciones más complejas como un auditoría o ataque al sitio web como se puede apreciar en la Fig. 15.

Now that we have already performed a scan of the web site (crawling) we could take further actions more complex like an audit or attack the web site as showed in Fig. 15.

Fig. 15 – Resultados del escaneo web (crawling) / Web scanning output

Al final del ciclo de pentesting e igualmente importante que las otras fases es crear un buen y claro informe que detalle las acciones realizadas, sistemas y vulnerabilidades descubiertas además de información de apoyo (información recogida).

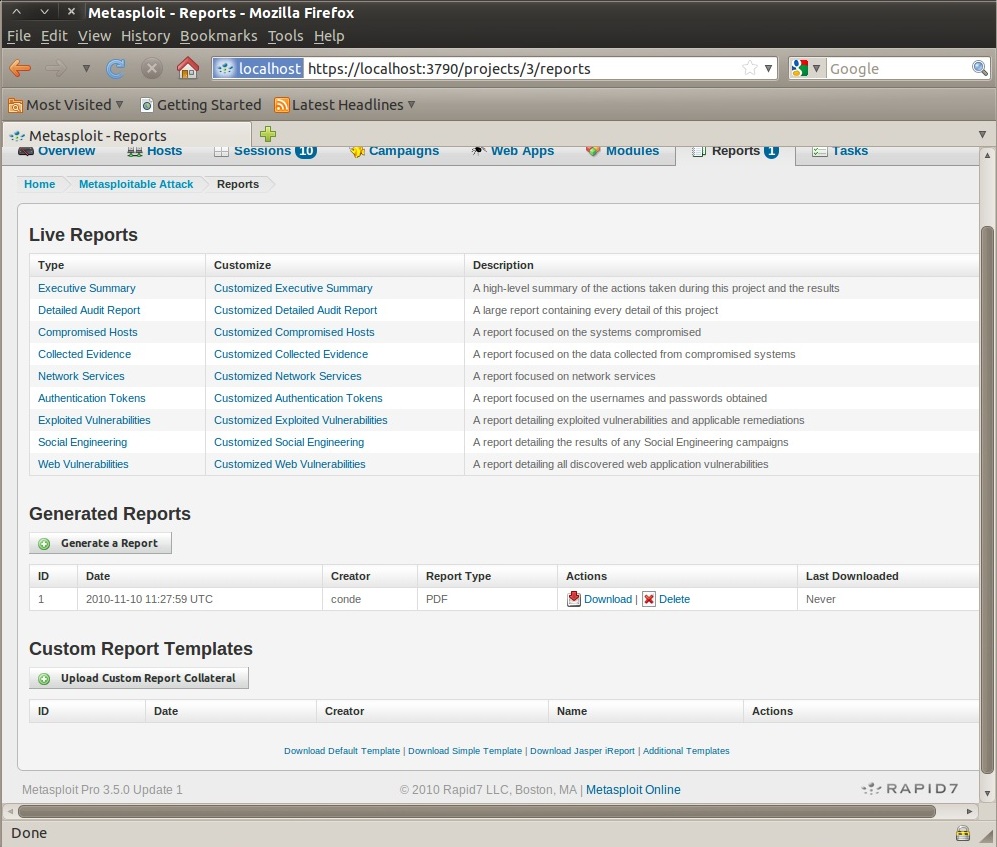
Metasploit PRO también nos ayuda en este aspecto ya que nos permite generar informes con todo lujo de detalles de forma rápida con todo el historial de nuestras actividades. La Fig. 16 nos muestra cómo generar informes con esta estupenda herramienta.

At the end of the pentesting cycle and equally important as other phases is to create a good and clear report describing all actions, systems and vulnerabilities discovered in addition to information collected.

Metasploit PRO also helps us here as it allows us to generate reports with all luxury of details quickly with the entire history of our activities. Fig. 16 shows us how to generate reports within this great tool.

Fig. 16 – Generando un informe / Report creation

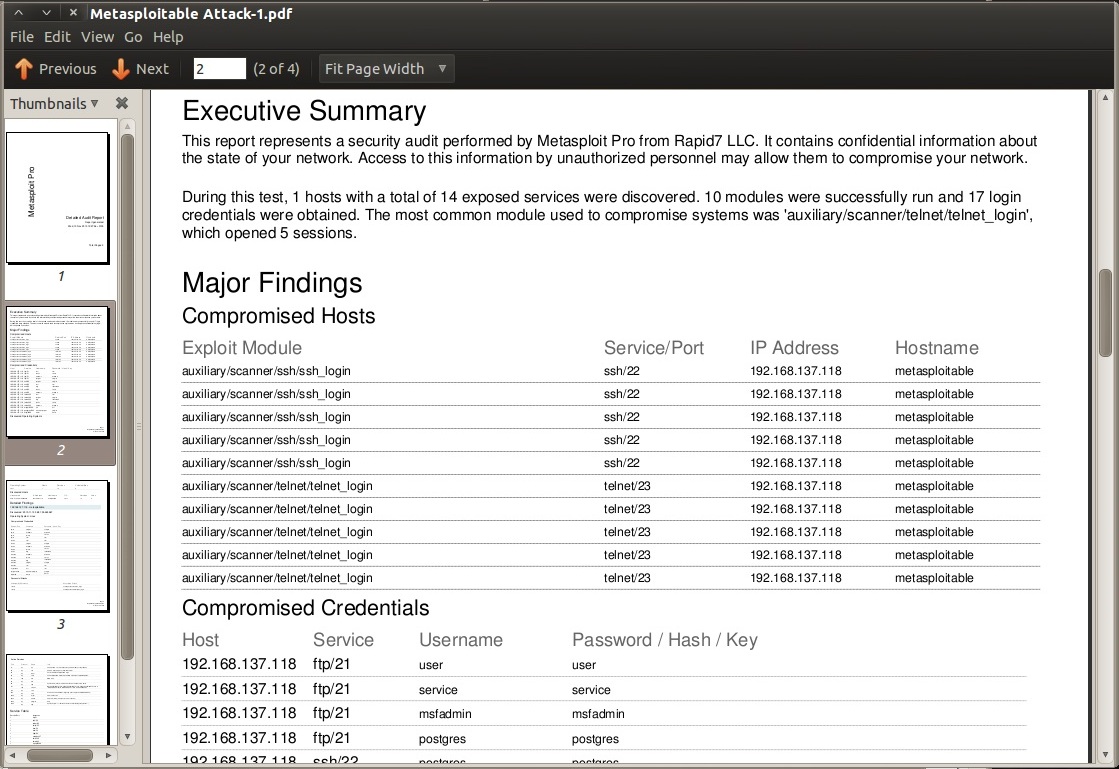
La Fig. 17 es un PDF que podemos enviar a nuestro cliente para que pueda leer cómo hemos comprometido su seguridad ;)

Fig. 17 is a PDF that we can send to our customer so he can read how we compromised their security ;)

Fig. 17 – Informe en PDF / PDF report

Como hemos podido apreciar a lo largo del post esta herramienta es fundamental para cualquier pentester profesional y posiblemente sea una de las herramientas más completas del mercado.

No he ejecutado ningún exploit a propósito ya que quería que el lector viera lo fácil que puede ser comprometer la seguridad de un sistema sin utilizar exploits. Admito que he utilizado una versión Linux vulnerable, pero aquellos lectores que sean pentester sabrán que no dista mucho de los entornos de sus clientes, probad a realizar auditorías de contraseñas :)

As we have seen in the post this tool is essential for any professional pentester and possibly one of the most comprehensive tools in the market

I have not run any exploit deliberately as I wanted to prove to the reader how easy it can be compromising the security of a system without using exploits. Admittedly, I used a vulnerable Linux version but those readers who are pentesters will know that this scenario is not far from real customer’s environments, try to perform passwords audit :)

Igualmente me he dejado muchas cosas en el tintero de esta formidable herramienta como son:

  • Integración con neXpose, escaneo de vulnerabilidades.
  • Pivoting (Proxy y VPN), utilizar un sistema comprometido para comprometer otros sistemas.
  • El modo Campaña, para lanzar ataques de ingeniería social y phishing.
  • Ataques coordinados entre varios pentesters.
  • Y muchas más cosas que podéis en la web oficial del producto.

Also I have left many things in the dark of this formidable tool as:

  • Integration with neXpose vulnerability scanning.
  • Pivoting (Proxy and VPN), use a compromised system to compromise other systems.
  • How to perform a campaign, to launch social engineering and phishing attacks.
  • Coordinated attacks between several pentesters, collaboration.
  • And many more things you can read on the product website.

Todas estas opciones y muchas más convierten a Metasploit PRO, al estar respaldada por metasploit, en producto líder de su categoría. Podríamos escribir un libro con todo lo que nos puede ofrecer esta herramienta :)

Para sacar el mayor rendimiento a Metasploit PRO es conveniente utilizarlo en Linux aunque también existe una versión Windows.

Agradecer a HD Moore y al equipo de Rapid7 al incluirme en la beta del programa y por convertir a metasploit en posiblemente el mejor “explotation framework” del mercado.

 ¿Cuál es tu explotation framework favorito y porque?

All of these options and many more make Metasploit PRO, supported by metasploit, a leading product in its class. We could write a book with all this tool can offer us :)

To get maximum performance of Metasploit PRO it is convenient to use a Linux system but there is also a Windows version as well.

Thanks HD Moore and the Rapid7 team for including me in the beta program and make metasploit possibly the best “exploitation framework” of the market.

Which is your favorite exploitation framework and why?

— Simon Roses Femerling

Posted in Hacking, Pentest, Security | Tagged , , , , , | Leave a comment