Inauguramos una nueva sección del blog con un aviso de seguridad en una aplicación Android vulnerable que descubrí hace unos meses, todo un ejemplo de desarrollo inseguro.
No soy muy dado a publicar avisos de seguridad por el amplio gasto de recursos que consumen y el poco ROI pero de vez en cuando publicaremos algo. Tenemos más 0days en el horno ;)
We are inaugurating a new section of the blog with a security advisory in a vulnerable Android app that I discovered a few months ago, a good example of insecure development practices.
I’m not too keen to publish security advisories for the broad spending of resources they consume and the little ROI but occasionally we will release some stuff. We have more 0days in the oven ;)
El 16 y 17 de Abril tuvo lugar en Miami la primera edición de Infiltrate organizada por ImmunitySec con la aspiración de ser el mejor congreso ofensivo y tengo que admitir que lo han conseguido y con nota!
The first edition of Infiltrate organized by ImmunitySec was held in Miami on 16 And 17 April with the aspiration of being the best offensive conference and I have to admit that they have exceeded my expectations!.
Es el primer congreso en el que he asistido a todas las charlas porque eran todas muy buenas, aunque no perfectas. Prácticamente casi todas las presentaciones utilizaban exploits y algunos eran 0day.
It is the first conference that I have attended all the talks because they were all very good but not perfect. Almost all presentations used exploits and some were 0day.
Mis presentaciones favoritas fueron del primer día (Rock’m Sock’m Robots: Exploiting the Android Attack Surface y The Listening) aunque las presentaciones del segundo día tampoco tenían desperdicio como: Bypassing Windows services protections o Infiltrating PHP.
My favorite presentations were on the first day (Rock’m Sock’m Robots: Exploiting the Android Attack Surface and The Listening) although the presentations of the second day were not wasted material either: Bypassing Windows services protections or Infiltrating PHP.
Desde luego ha sido uno de los mejores congresos que he asistido, no sólo por la calidad técnica sino por el trato recibido ya que la gente de ImmunitySec ha realizado un gran esfuerzo poniendo toda la carne en el asador, y se han preocupado en todo momento en que los asistentes estuviéramos cómodos, por lo que aprovecho para felicitar a todo el equipo de Immunity por el gran evento! :)
Sin duda un congreso en mi lista de obligados, hasta el año que viene!
For sure one of the best conferences I have ever attended not only by the technical quality but by the treatment received by the people of ImmunitySec, who made a great effort to make sure all attendees were comfortable. Because of this I would like to take this opportunity to give my congratulations to all the Immunity team for the big event! :)
No doubt a mandatory conference on my list, until next year!
Aprovechando mi asistencia al congreso de Infiltrate 2011 realize una de las formaciones que Immunitysec ofrecía, su aclamado curso Unethical Hacking. Este curso es bastante diferente de otros cursos de seguridad ya que es totalmente ofensivo y está enfocado a escribir exploits para Windows.
Taking advantage of my attendance to Infiltrate 2011 I registered for one of the trainings that Immunitysec offered its acclaimed Unethical Hacking class. This course is quite different than other security courses because it is totally offensive and focused on writing exploits for Windows.
Generalmente este curso se realiza en 5 días pero en este caso duro 4 días y se nota esa falta ,pero a pesar de ello fue un curso extremadamente práctico e interesante.
This course is usually done in 5 days, but in this case was 4 days only and you could feel the lack of that day, but nevertheless it was an extremely practical and interesting course.
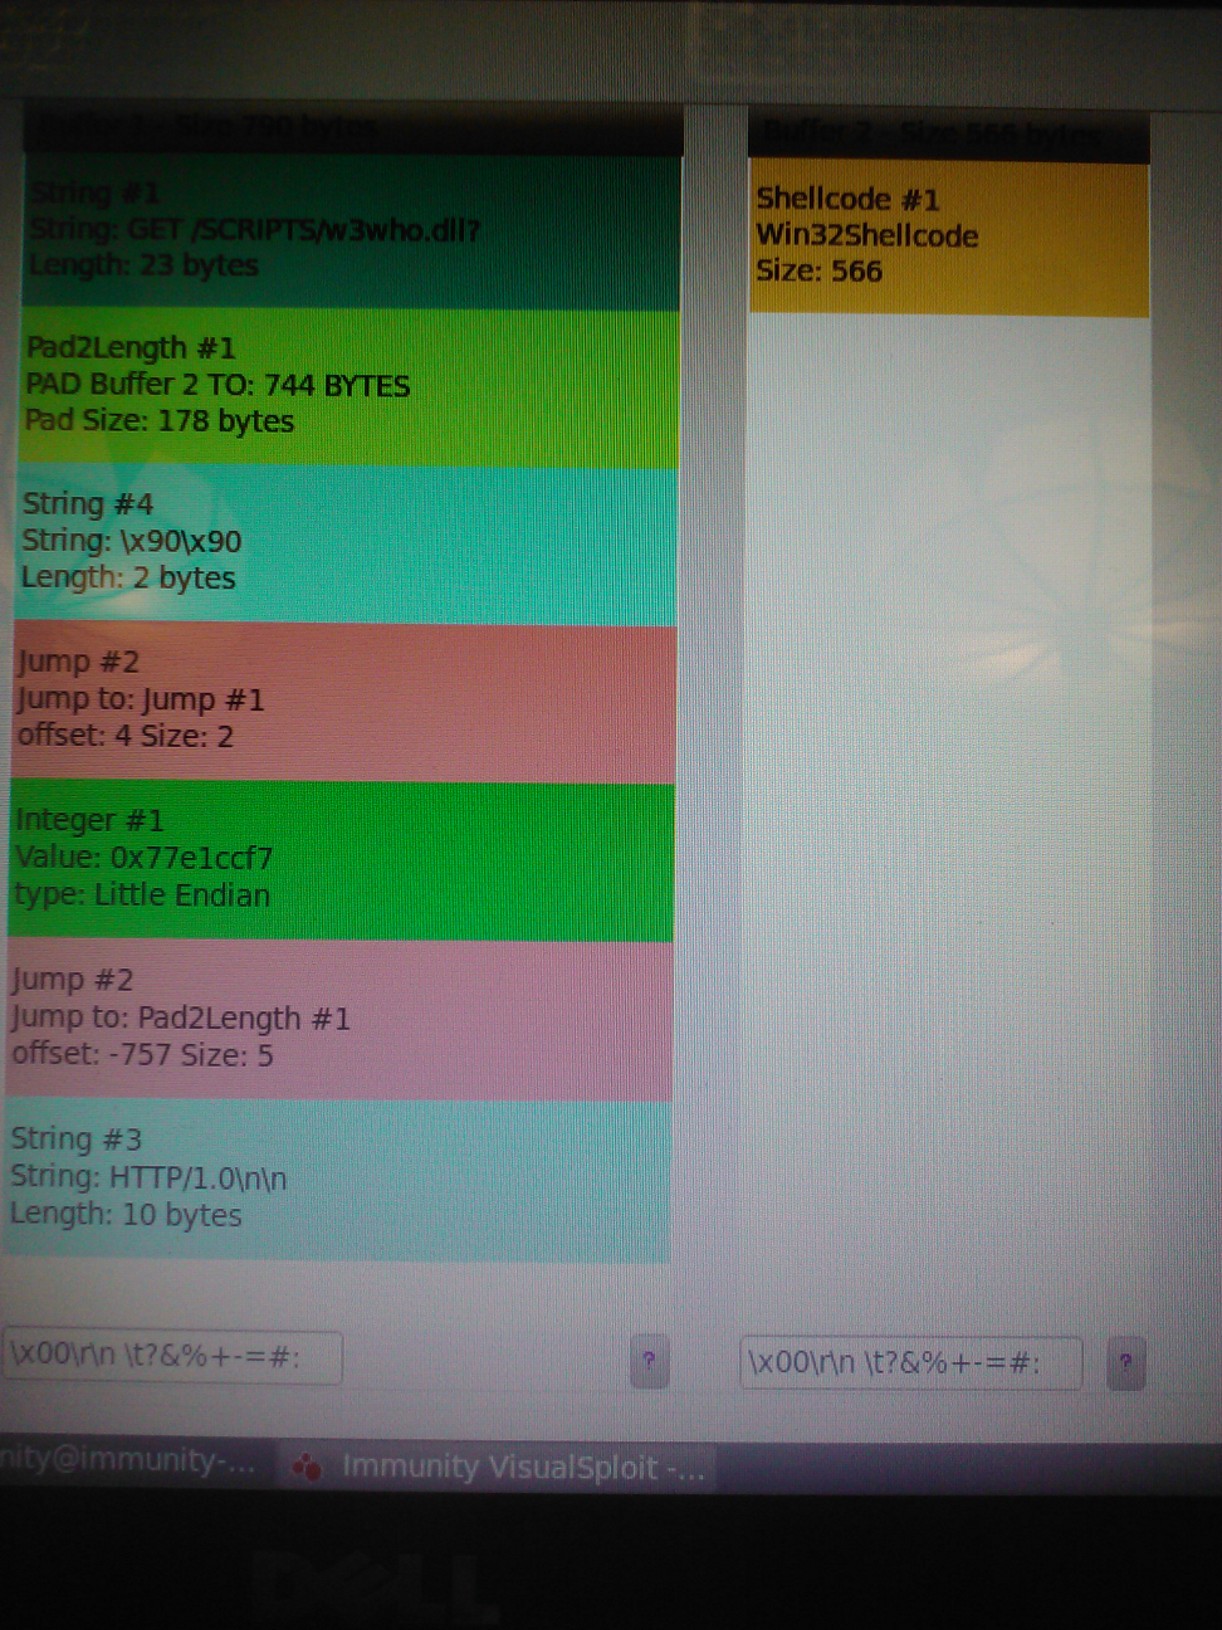
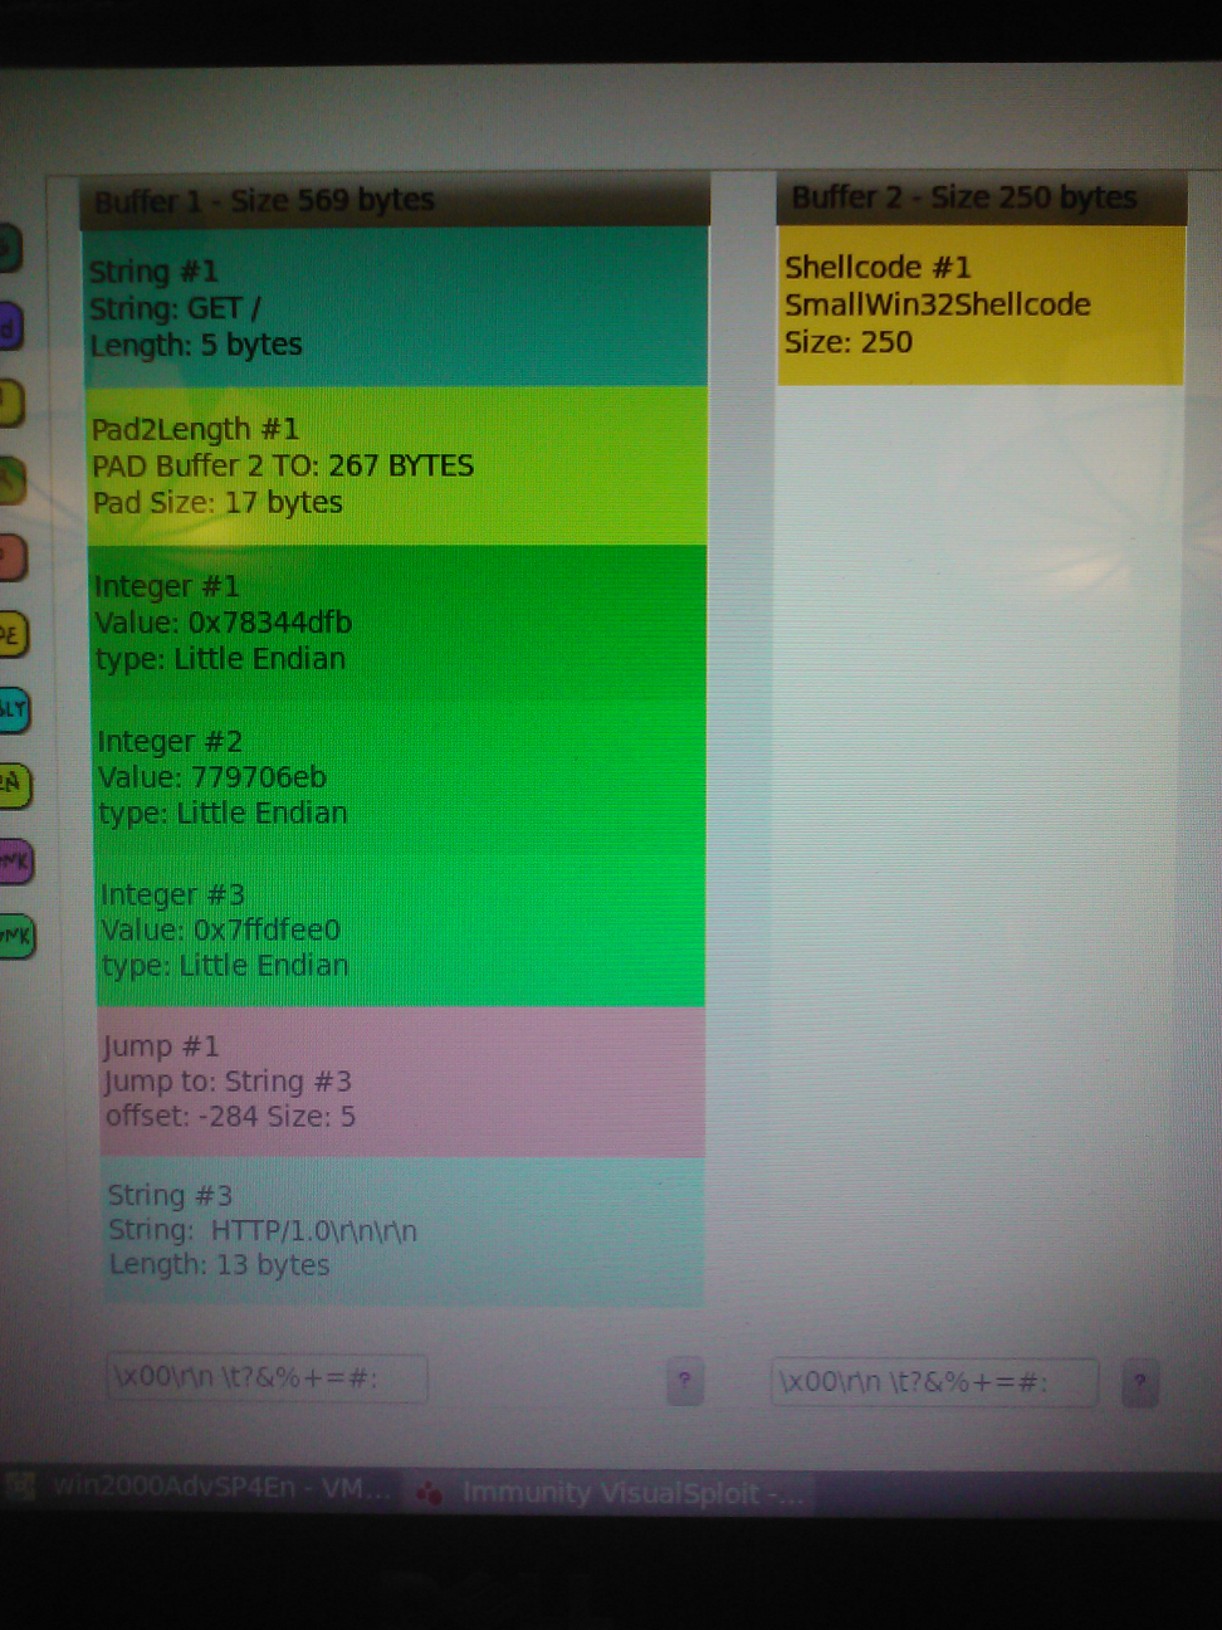
El primer día te dan una carpeta con más de 500 páginas sobre escribir exploits y shellcode en Windows (Stack, SEH, etc.) y el uso de Canvas, pero aquí termina la teoría ya que el curso está pensado para que lo leas por tu cuenta. Pasadas un par de horas de teoría del primer día comienza el primer ejercicio que consiste en escribir un exploit para un simple stack overflow utilizando VisualSploit e Immunity Debugger. Los días 2 y 3 continúas escribiendo exploits hasta un total de 7 exploits como un loco.
The first day you are given a folder with more than 500 pages on writing exploits and shellcode on Windows (Stack, SEH, etc.) and the use of Canvas, but here ends the theory as the course is designed to enable you to read it on your own. Past a couple of hours of theory of the first day we started the first exercise that consists of writing an exploit for a simple stack overflow using VisualSploit and Immunity Debugger. Days 2 and 3 continues writing exploits for a total of 7 exploits like madness.
El 4 día se enfocó al uso de Canvas y se realizó un pequeño concurso de hacking web por un magnifico premio, un Silica.
Lo cierto es que es un curso que recomiendo si quieres conocer el arte de escribir exploits para Windows o el uso de las herramientas de Immunity como VisualSploit, Immunity Debugger o Canvas. No hace falta tener experiencia en programación pero ayuda.
Desde aquí dar las gracias al equipo de Immunity por el curso y nos vemos en el Master Class cuando pueda :)
The 4 day focused on the use of Canvas and a small web hacking contest was held for a magnificent award, Silica.
The truth is that it is a course which I recommend if you want to know the art of writing exploits for Windows or the use of the tools of Immunity VisualSploit, Immunity Debugger or Canvas. There is no need to have experience in programming but it helps.
From here I would to thanks the Immunity team for the great course and see you in the Master Class when I can :)
— Simon Roses Femerling
Aquí os dejo unos screenshots que os darán una shell pero no son 0days ;)
Here are a few screenshots that you will give a shell but aren’t 0days ;)