AppSec: Overview of Fuzzing Frameworks

[Español] En los últimos años el fuzzing se ha convertido en la mejor y más rápida (relativamente) técnica para descubrir fallos de seguridad, por lo que he pensado que sería un buen tema para introducir algunos conceptos y  herramientas para luego entrar en más detalle en futuros posts.

[English] In recent years fuzzing has become the best and (relatively) quickest technique to discover security vulnerabilities, so I thought it would be a good topic to write a post about it to introduce some concepts and tools to then go into more details in future posts.

Aparte de mis frecuentes auditorías de código también dedico tiempo al fuzzing para identificar vulnerabilidades en todo tipo de aplicaciones con buenos resultados :) Imagino que el lector a estas alturas habrá oído hablar del Microsoft SDL, donde se especifica que uno de los controles de seguridad obligatorios es hacer fuzzing de la aplicación. Es por ello que Microsoft ha desarrollo algunos de los mejores fuzzers del mercado, como son SAGE y FuzzGuru entre otros, aunque por desgracia solo están disponibles internamente en la compañía pero existen algunas interesantes alternativas como veremos en la sección de recomendados.

Apart from my frequent code reviews I also spend time fuzzing to identify vulnerabilities in all kinds of applications with good results :) I assume the reader at this point has heard of Microsoft SDL, which mandates that one of the security gates is to fuzz the application. This is why Microsoft has developed some of the best fuzzers in the market, such as SAGE and FuzzGuru among others, although unfortunately only internally available in the company but there are some interesting alternatives as we will see in the section of recommended.

A la hora de realizar fuzzing debemos tener una clara estrategia para que sea efectivo o podríamos estar perdiendo el tiempo. Debemos tener claro:

  • Qué interfaces de la aplicación queremos fuzzear (ficheros, protocolos, registro, etc.)
  • Si nuestro fuzzer es capaz de generar datos malformados válidos para la aplicación
  • Cuántas pruebas estamos ejecutando por minuto
  • Si hemos definido el “número mágico” para detener las pruebas
  • A qué nivel de profundidad estamos llegando en la aplicación (Code coverage)
  • De qué capacidades de monitorización disponemos
  • Si disponemos de herramientas apropiadas para analizar un crash

When it comes to fuzzing we must have a clear strategy to be effective or we could be wasting time. We must be clear on:

  • What application interfaces we want to fuzz (files, Protocols, registry, etc.)
  • If our fuzzer is able to generate valid malformed data for the application
  • How many test cases are we running per minute
  • If we have defined the “magic number” to stop testing
  • What level of application depth  we are reaching (Code coverage)
  • If we have monitoring capabilities
  • If we have the appropriate tools to analyze a crash

Éstas son algunas de las cuestiones que nuestra estrategia debe tener en cuenta para sacarle el mayor partido al tiempo de fuzzing ya que no es infinito. En mi caso he construido una pequeña granja fuzzing que me permite escalar y realizar diferentes pruebas al mismo tiempo, bendita sea la virtualización!

These are some of the issues that our strategy must take into account to get the most out of the fuzzing time because is not infinite. In my case I have built a small fuzzing farm that allows me to scale and perform various tests at the same time, blessed be the virtualization!

De vez en cuando hasta un fuzzer tonto es capaz de descubrir vulnerabilidades, pero por lo general obtendremos mejores resultados con un fuzzer inteligente que entienda la información que requiere la aplicación y pueda manipularla. La mayoría de fuzzers recomendados están dentro de la categoría de fuzzers inteligentes, aunque sin duda los fuzzers tontos nos pueden ser de gran utilidad también. Si tenemos tiempo es recomendable probar diferentes tipos de fuzzers para el mismo objetivo.

From time to time a dumb fuzzer is able to discover vulnerabilities but usually we get better results with a smart fuzzer who understands the data required by the application and is able to mutate it. Most of the below recommended fuzzers are within the category of smart fuzzers but certainly dumb fuzzers can be very useful too. If we have time we recommend trying different types of fuzzers for the same target.

Existen muchos más fuzzers de los aquí mencionados pero en mi opinión éstos son algunos de los mejores y estoy seguro que el lector les encontrará utilidad. Si encuentras un ODay no  olvides enviármelo ;)

There are many more fuzzers of the here mentioned but in my opinion these are some of the best and I am sure the reader will find them useful. If you find an ODay don’t forget send it my way ;)

Fuzzer Frameworks y Recursos Recomendados / Fuzzer Frameworks and Recommended Resources

Y tú qué fuzzer framework utilizas?

What fuzzer framework do you use?

— Simon Roses Femerling
Posted in Hacking, Pentest, SDL, Security, Technology | Tagged , , , , , | Leave a comment

AppSec: Mobile Apps InSecure Development Practices

[Español] Uno de mis proyectos personales es analizar la seguridad de dispositivos móviles, y los lectores del blog ya lo habrán notado por varios posts al respecto sobre malware, vulnerabilidades y crackmes.

[English] One of my personal projects is to analyze the security of mobile devices, and the readers of the blog will have already noticed by several posts about it on malware, vulnerabilities and crackmes.

La semana pasada se publicó un artículo que he escrito sobre inseguridad en Apps móviles para Android y Windows Phone 7 en la revista (IN)Secure y que estoy seguro el lector encontrará interesante.

Last week an article I have written about insecurity in Mobile Apps for Android and Windows Phone 7 was published in the (IN)Secure magazine that I am sure the reader will find interesting.

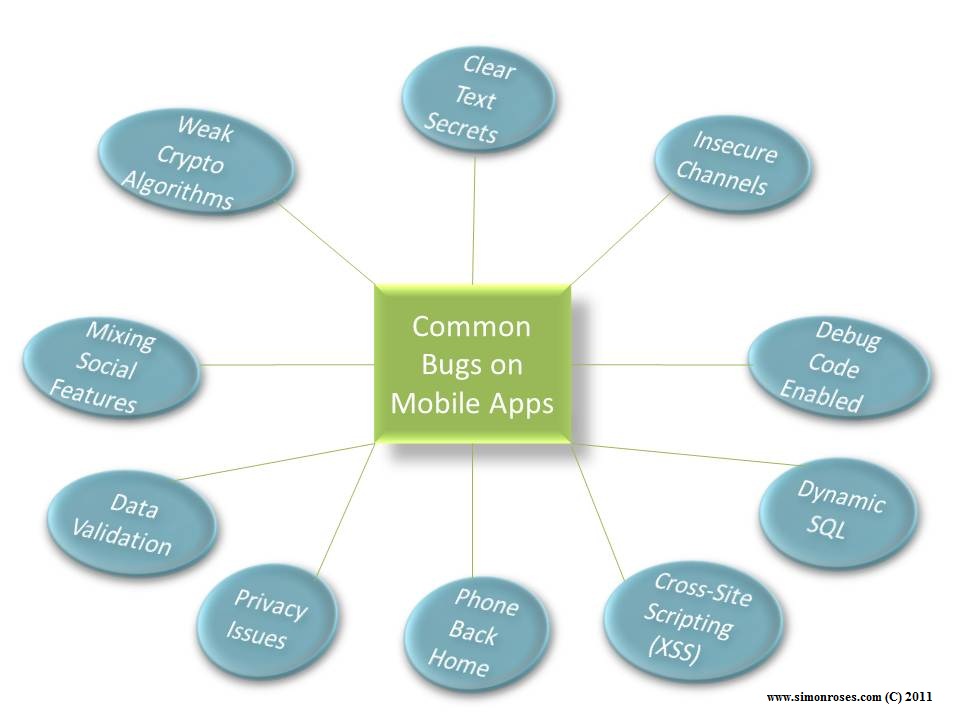
En la Fig. 1 se puede apreciar vulnerabilidades que aparecen con frecuencia en Apps. Desgraciadamente demasiadas Apps se desarrollan sin pensar en la seguridad ya sea por desconocimiento o pereza, pero es un problema serio para las organizaciones cuando pensamos la cantidad de dispositivos móviles (Smartphones y tabletas) que se utilizan a diario con información sensible con unas barreras de seguridad mínimas o nulas. Todos los detalles se encuentran en el artículo mencionado.

In Fig. 1 you can see vulnerabilities that appear frequently in Apps. Unfortunately too many Apps are developed without thinking about security either by ignorance or laziness, but it’s a serious problem for most organizations when you think the number of mobile devices (Smartphone and tablets) used on a daily basis containing sensitive information with a minimum or no safety barriers. For more details please read the article.

  Fig. 1  – Mapa de Vulnerabilidades en Apps / Apps Vulnerability Map

Aparte de la información del artículo tengo más material nuevo que espero presentar en futuros artículos y conferencias. Atentos a las noticias en el blog :)

Y tú que piensas de la seguridad y privacidad de las Apps?

Besides the information presented in the article I have more new material which I hope to submit in future articles and conferences. Pay attention to blog updates :)

And what do you think of the safety and privacy of Apps?

— Simon Roses Femerling

Posted in Hacking, Pentest, Security, Technology | Tagged , , , , , , | Leave a comment

FUD on Cloud Security

[Español] Últimamente he asistido a varios eventos sobre seguridad en la Nube (Cloud) y sorprende el alto grado de FUD que existe sobre este tema. La Nube no es un concepto o tecnología nueva sino más bien un uso eficiente de una serie de tecnologías que todos conocemos como Servicios Web, virtualización, etc.

[English] Lately I have attended several events on Cloud security and it is surprising the high degree of FUD that exists on this subject. The cloud is not a new concept or technology, but rather an efficient use of a number of technologies that we all know well such as Web services, virtualization, etc.

El principal problema de las empresas a la hora de utilizar la Nube es la supuesta pérdida de control de su información, que en la mayoría de los casos no es real, un miedo provocado por un desconocimiento en la materia.

The main problem of companies using the cloud is the alleged loss of control of their information, which in the majority of cases is not real, and this fear is caused by a lack of knowledge on the subject.

Las empresas deben realizar un análisis sobre qué aplicaciones e información pueden utilizar en la Nube, que en muchas ocasiones son la mayoría de aplicaciones corporativas ya que no utilizan información sensible. Para ello la empresa debe conocer su información y establecer una política de clasificación de información.

Companies must perform an analysis on which applications and information can be used in the cloud, most of corporate applications can as they do not use sensitive information. While doing so the company must know their information and establish a Data Classification Policy.

Es frecuente en este tipo de eventos oír a personas que protestan por perder el control de su información y su ubicación e incluso piden que se audite a los proveedores de servicios en la Nube cuando seguramente en sus propias organizaciones no protegen adecuadamente todos los lugares donde almacenan su información, y bien seguro no auditan a sus proveedores o empresas aliadas que suelen tener acceso a la redes corporativas.

It is common in this type of event to hear people protesting due to the loss of control of their information and its location and even requesting cloud vendors to be audited when probably in their own organizations they do not adequately protect all the places where they stored information, and for sure they do not audit their vendors and partners that usually have access to their corporate networks.

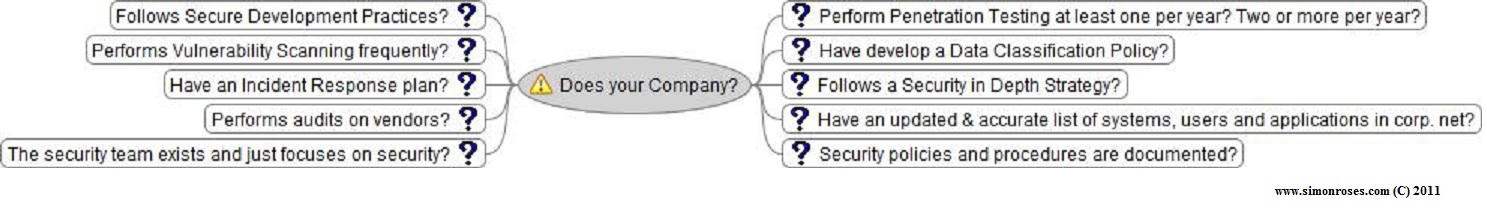
En la Fig. 1 se plantean diversas cuestiones de seguridad que generalmente demasiadas empresas de todos los tamaños no realizan o ni siquiera se plantean. Es complicado entender la misteriosa Nube cuando estas cuestiones con décadas de existencia aún no son entendidas por las organizaciones.

In Fig. 1 we arise various security issues that usually too many companies of all sizes do not perform or don’t care. It is difficult to understand the mysterious ways of the cloud when these issues with decades of existence are not yet understood by organizations.

Fig.1 – Grado de madurez de la seguridad en una empresa / Degree of security maturity in an enterprise

Es cierto que la Nube puede ayudar a muchas organizaciones en el ahorro de costes y agilidad, pero también puede ayudar a ser más seguras. Algunos puntos a tener en cuenta son:

  • Antes debemos conocer nuestra organización (activos, riesgos, información, aplicaciones, etc.) para tomar las decisiones adecuadas sobre qué subir a la Nube.
  • Es cierto que en la Nube podemos perder la visibilidad de la ubicación de nuestra información pero no debería ser problema, ya que existen mecanismos de seguridad efectivos como la criptografía y algunos proveedores pueden establecer criterios de localización.
  • Es clave la correcta selección de un proveedor de la Nube que nos pueda dar garantías y responda en las incidencias.
  • Un buen contrato (SLA) es vital.
  • Tenemos que ser racionales a la hora de establecer mecanismos de seguridad en la Nube como lo haríamos en nuestras organizaciones. La tecnología existe pero debemos utilizarla correctamente.

It is true that the cloud can help many organizations in saving costs and being more agile but it can also help be more secure. Some points to consider are:

  • Before moving to the cloud we must know our Organization (assets, risks, information, applications, etc.) to take the appropriate decisions of what to move to the cloud.
  • It is true that in the cloud we can lose visibility of the location of our information, but it should not be problem since there are effective security mechanisms such as cryptography, and some cloud vendors can establish location criteria.
  • It is key the correct selection of a cloud provider that can give us guarantees and responds to incidents.
  • A good contract (SLA) is vital.
  • We must be rational in establishing security mechanisms in the cloud as we would in our organizations. The technology exists but we must use it correctly.

Sin duda la Nube es una tema interesante y de moda que cada día mas organizaciones se plantean utilizar por lo que se debe perder este miedo absurdo. Aquellas organizaciones que no sepan apreciar las bondades de la Nube perderán en innovación.

Tu organización se plantea utilizar la Nube y para qué?

No doubt the cloud is a hot topic that every day more organizations think of using but first we should lose this absurd fear. Those organizations that do not recognize the benefits of the cloud will lose their innovation.

Does your organization use the cloud and for what?

— Simon Roses Femerling

Posted in Business, Economics, Pentest, Security, Technology | Tagged , , | Leave a comment